Halloween Special Sale 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: sale75best

Free Cisco 300-710 Practice Exam with Questions & Answers | Set: 13

Questions 121

An engineer is deploying a Cisco ASA Secure Firewall module. The engineer must be able to examine traffic without impacting the network, and the ASA has been deployed with a single context. Which ASA Secure Firewall module deployment mode must be implemented to meet the requirements?

Options:
A.

Transparent mode with inline tap monitor-only mode

B.

Routed mode with passive monitor-only mode

C.

Transparent mode with passive monitor-only mode

D.

Routed mode with inline tap monitor-only mode

Cisco 300-710 Premium Access
Questions 122

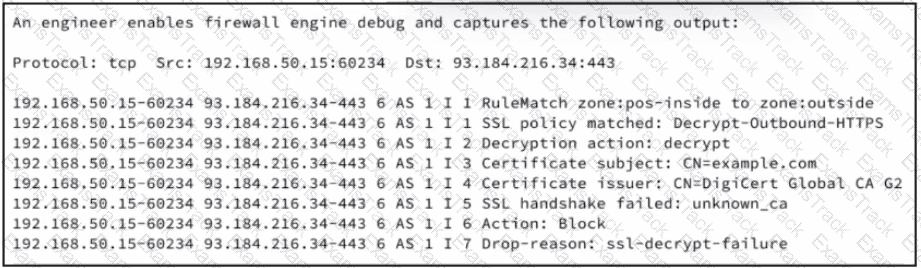
Refer to the exhibit.

300-710 Question 122

Security engineer is investigating an issue where outbound HTTPS traffic from an endpoint using network 192.168.50.0/24 is being blocked. The Cisco Secure Firewall Threat Defense is configured with a TLS decryption policy applied to all outbound web traffic. An engineer enables firewall engine debug and captures the output. Which action must be performed to resolve the issue?

Options:
A.

Export the TLS re-signing CA certificate used by the SSL policy and deploy it to the trusted root store on the POS terminals.

B.

Enroll the FTD re-signing CA from the corporate internal CA and redeploy the SSL policy, trusted in the Windows certificate store.

C.

Add DigiCert Global CA G2 to the trusted CA list in the SSL policy to accept the external issuer during re-signing and complete the handshake.

D.

Add the destination IP range of POS terminal traffic to a URL-category-based SSL rule with the action set to Do Not Decrypt.

Questions 123

An engineer is restoring a Cisco FTD configuration from a remote backup using the command restore remote-manager-backup location 1.1.1.1 admin /volume/home/admin BACKUP_Cisc394602314.zip on a Cisco FMG. After connecting to the repository, an error occurred that prevents the FTD device from accepting the backup file. What is the problem?

Options:
A.

The backup file is not in .cfg format.

B.

The backup file is too large for the Cisco FTD device

C.

The backup file extension was changed from tar to zip

D.

The backup file was not enabled prior to being applied

Questions 124

What is the purpose of the IRB feature in next-generation firewall?

Options:
A.

To allow multiple physical interfaces to be part of the same VLAN

B.

To enable transparent bridging between two Layer 2 interfaces

C.

To block routing between two Layer 3 interfaces

D.

To configure NAT in transparent mode

Questions 125

An engineer has been asked to show application usages automatically on a monthly basis and send the information to management What mechanism should be used to accomplish this task?

Options:
A.

event viewer

B.

reports

C.

dashboards

D.

context explorer

Questions 126

A network administrator wants to configure a new Secure Firewall Threat Defense instance, which is managed by Cisco Secure Firewall Management Center, to load balance internet-bound traffic across multiple zones. Secure Firewall is connected to upstream ISP devices in multiple Zones. Which action must be taken to meet the requirement?

Options:
A.

Configure multiple static default routes to multiple zones towards upstream ISP devices.

B.

Enable BGP and OSPF towards upstream ISP devices.

C.

Implement OSPF and static route towards to upstream ISP devices.

D.

Add multiple dynamic routes set up via flex configuration to multiple zones.

Questions 127

Refer to the exhibit.

What must be done to fix access to this website while preventing the same communication to all other websites?

Options:
A.

Create an intrusion policy rule to have Snort allow port 80 to only 172.1.1 50.

B.

Create an access control policy rule to allow port 80 to only 172.1.1 50.

C.

Create an intrusion policy rule to have Snort allow port 443 to only 172.1.1.50

D.

Create an access control policy rule to allow port 443 to only 172.1.1 50

Questions 128

What is a result of enabling Cisco FTD clustering?
Options:
A.

For the dynamic routing feature, if the master unit fails, the newly elected master unit maintains all existing connections.

B.

Integrated Routing and Bridging is supported on the master unit.

C.

Site-to-site VPN functionality is limited to the master unit, and all VPN connections are dropped if the master unit fails.

D.

All Firepower appliances can support Cisco FTD clustering.

Questions 129

300-710 Question 129

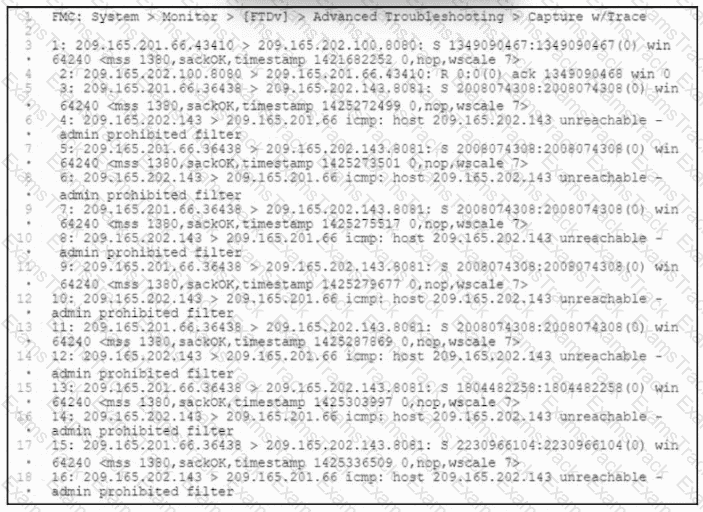
Refer to the exhibit. Users attempt to connect to numerous external resources on various TCP ports. If the users mistype the port, their connection closes immediately, and it takes more than one minute before the connection is torn down. An engineer manages to capture both types of connections as shown in the exhibit. What must the engineer configure to lower the timeout values for the second group of connections and resolve the user issues?

Options:
A.

outbound access rule that allows the entire ICMP protocol suite

B.

inbound access rule that allows ICMP Type 3 from outside

C.

inbound access rule that allows TCP reset packets from outside

D.

outbound access rule with the Block with reset action

Questions 130

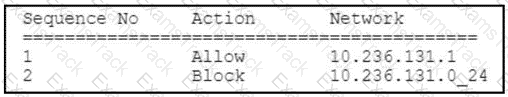
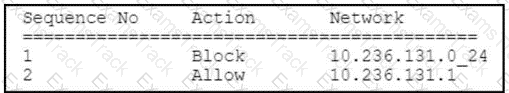
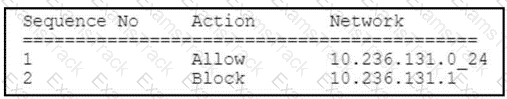
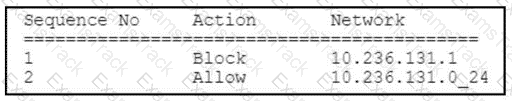
A security engineer must create an access list object in Cisco Secure Firewall Management Center to allow traffic to IP address 10.236.131.1 but block traffic to IP address 10.236.131.0/24. Which access control entries must the engineer create?

A)
300-710 Question 130

B)

300-710 Question 130

C)

300-710 Question 130

D)

300-710 Question 130

Options:
A.

Option A

B.

Option B

C.

Option C

D.

Option D