Halloween Special Sale 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: sale75best

Free Cisco 300-710 Practice Exam with Questions & Answers | Set: 8

Questions 71

An engineer defines a new rule while configuring an Access Control Policy. After deploying the policy, the rule is not working as expected and the hit counters associated with the rule are showing zero. What is causing this error?

Options:
A.

Logging is not enabled for the rule.

B.

The rule was not enabled after being created.

C.

The wrong source interface for Snort was selected in the rule.

D.

An incorrect application signature was used in the rule.

Cisco 300-710 Premium Access
Questions 72

When creating a report template, how can the results be limited to show only the activity of a specific subnet?

Options:
A.

Create a custom search in Firepower Management Center and select it in each section of the report.

B.

Add an Input Parameter in the Advanced Settings of the report, and set the type to Network/IP.

C.

Add a Table View section to the report with the Search field defined as the network in CIDR format.

D.

Select IP Address as the X-Axis in each section of the report.

Questions 73

An organization recently implemented a transparent Cisco FTD in their network.

They must ensure that the device does not respond to insecure SSL/TLS protocols.

Which action accomplishes the task?

Options:
A.

Modify the device ' s settings using the device management feature within Cisco FMC to force onlysecure protocols.

B.

Use the Cisco FTD platform policy to change the minimum SSL version on the device to TLS 1.2.

C.

Enable the UCAPL/CC compliance on the device to support only the most secure protocols available.

D.

Configure a FlexConfig object to disable any insecure TLS protocols on the Cisco FTD device.

Questions 74

What is the difference between inline and inline tap on Cisco Firepower?

Options:
A.

Inline tap mode can send a copy of the traffic to another device.

B.

Inline tap mode does full packet capture.

C.

Inline mode cannot do SSL decryption.

D.

Inline mode can drop malicious traffic.

Questions 75

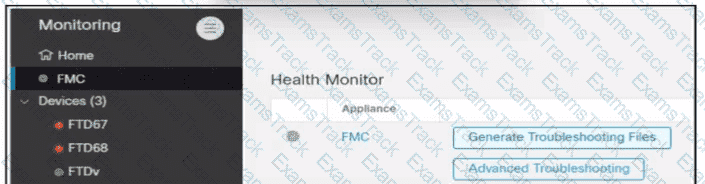
Refer to the exhibit.

300-710 Question 75

An engineer generates troubleshooting files in Cisco Secure Firewall Management Center (FMC). A successfully completed task Is removed before the files are downloaded. Which two actions must be taken to determine the filename and obtain the generated troubleshooting files without regenerating them? (Choose two.)

Options:
A.

Use an FTP client Hi expert mode on Secure FMC lo upload the files to the FTP server.

B.

Go to the same screen as shown in the exhibit, click Advanced Troubleshooting, enter the rile name, and then start the download

C.

Connect to CU on the FTD67 and FTD66 devices and copy the tiles from flash to the PIP server.

D.

Go to expert mode on Secure FMC. list the contents of/Var/common, and determine the correct filename from the output

E.

Click System Monitoring, men Audit to determine the correct filename from the line containing the Generate Troubleshooting Files string.

Questions 76

Which default action setting in a Cisco FTD Access Control Policy allows all traffic from an undefined application to pass without Snort Inspection?

Options:
A.

Trust All Traffic

B.

Inherit from Base Policy

C.

Network Discovery Only

D.

Intrusion Prevention

Questions 77

An engineer must build redundancy into the network and traffic must continuously flow if a redundant switch in front of the firewall goes down. What must be configured to accomplish this task?

Options:
A.

redundant interfaces on the firewall cluster mode and switches

B.

redundant interfaces on the firewall noncluster mode and switches

C.

vPC on the switches to the interface mode on the firewall duster

D.

vPC on the switches to the span EtherChannel on the firewall cluster

Questions 78

An engineer must configure a new identity policy in Cisco Firepower Management Center. Active authentication must be configured by using a Kerberos connection. Which two realms must be configured? (Choose two.)

Options:
A.

Directory password

B.

Active directory join password

C.

Active directory primary domain

D.

Active directory join username

E.

Directory username

Questions 79

Which policy rule is included in the deployment of a local DMZ during the initial deployment of a Cisco NGFW through the Cisco FMC GUI?

Options:
A.

a default DMZ policy for which only a user can change the IP addresses.

B.

deny ip any

C.

no policy rule is included

D.

permit ip any

Questions 80

An administrator is attempting to remotely log into a switch in the data centre using SSH and is unable to connect. How does the administrator confirm that traffic is reaching the firewall?

Options:
A.

by running Wireshark on the administrator ' s PC

B.

by performing a packet capture on the firewall.

C.

by running a packet tracer on the firewall.

D.

by attempting to access it from a different workstation.