examstrack logo
An administrator must use Cisco FMC to install a backup route within the Cisco FTD to route traffic in case of a routing failure with the primary route. Which action accomplishes this task?
An engineer must deny ICMP traffic to the networks of separate departments that use Cisco Secure Firewall Management Center. The engineer must use the same object on the relevant device for each network. What must be configured in Secure Firewall Management Center?
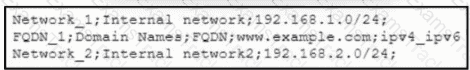
Refer to the exhibit. An engineer must import three network objects into the Cisco Secure Firewall Management Center by using a CSV file. Which header must be configured in the CSV file to accomplish the task?
Refer to the exhibit.
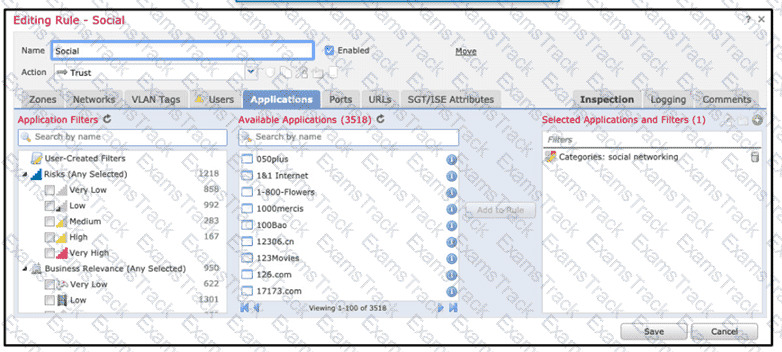
An organization has an access control rule with the intention of sending all social media traffic for inspection After using the rule for some time, the administrator notices that the traffic is not being inspected, but is being automatically allowed What must be done to address this issue?
An engineer Is configuring a Cisco FTD device to place on the Finance VLAN to provide additional protection tor company financial data. The device must be deployed without requiring any changes on the end user workstations, which currently use DHCP lo obtain an IP address. How must the engineer deploy the device to meet this requirement?
Refer to the exhibit.
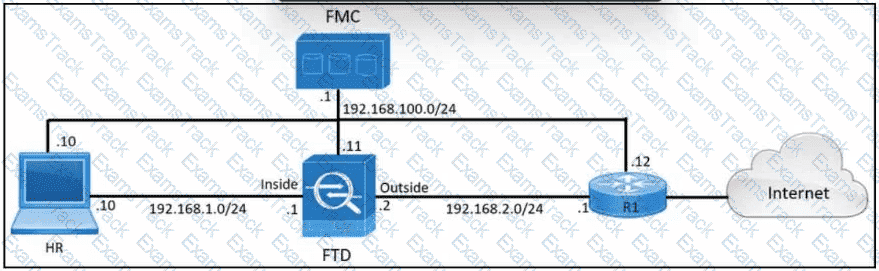
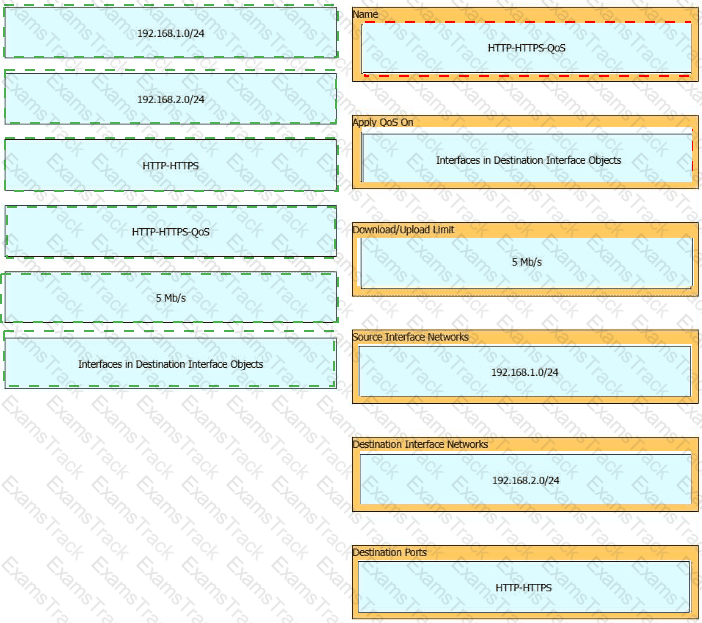
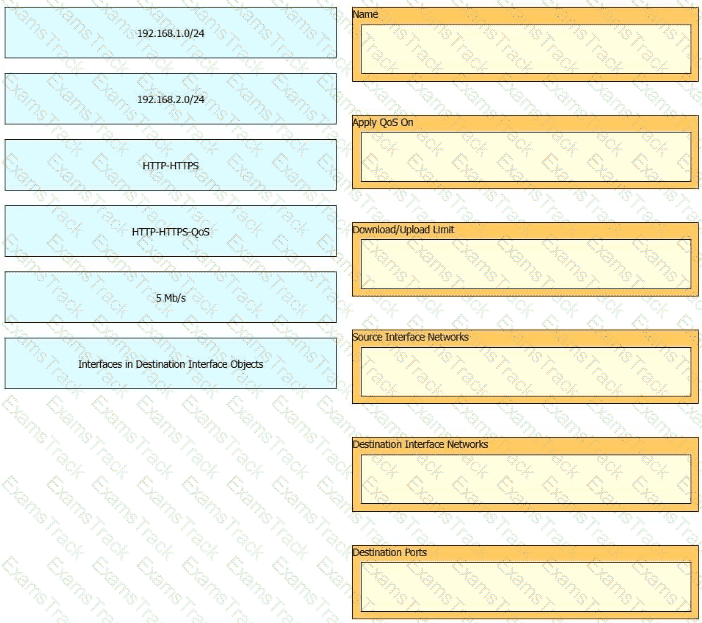
An engineer must create a QoS policy in Cisco Secure Firewall Management Center to limit HTTP and HTTPS traffic originating from users in the HR department. The download and upload limits for HTTP and HTTPS traffic must both be set to 5 Mb/s. Drag and drop the values onto the corresponding QoS rule settings.
A network engineer is configuring URL Filtering on Firepower Threat Defense. Which two port requirements on the Firepower Management Center must be validated to allow communication with the cloud service? (Choose two.)
What is the advantage of having Cisco Firepower devices send events to Cisco Threat response via the security services exchange portal directly as opposed to using syslog?
What is the disadvantage of setting up a site-to-site VPN in a clustered-units environment?
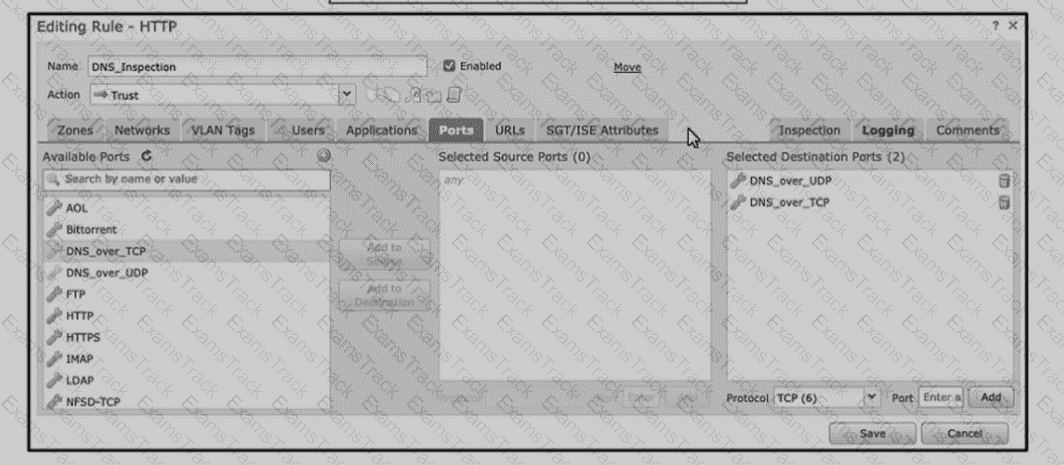
Refer to the exhibit An engineer is modifying an access control pokey to add a rule to inspect all DNS traffic that passes through the firewall After making the change and deploying thepokey they see that DNS traffic is not bang inspected by the Snort engine What is the problem?
|
PDF + Testing Engine
|
|---|
|
$43.75 |
|
Testing Engine
|
|---|
|
$33.75 |
|
PDF (Q&A)
|
|---|
|
$28.75 |
Cisco Free Exams |
|---|
|
Copyright © 2026 Examstrack. All Rights Reserved
TESTED 03 Nov 2026