Halloween Special Sale 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: sale75best

Free Cisco 300-710 Practice Exam with Questions & Answers | Set: 6

Questions 51

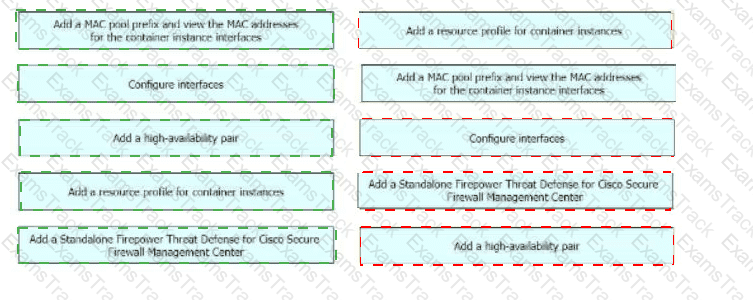
A network engineer is deploying a Cisco Firepower 4100 appliance and must configure a multi-instance environment for high availability. Drag and drop me actions from the left into sequence on the right far this configuration.
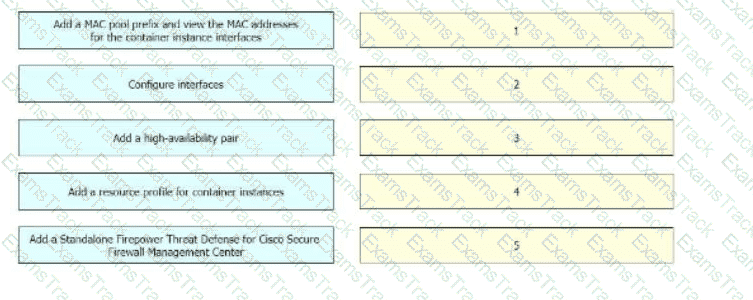
300-710 Question 51

Options:
Cisco 300-710 Premium Access
Questions 52

An engineer wants to convert a Cisco Secure Firewall Threat Defense device that is currently managed by Cisco Secure Firewall Management Center from routed mode to transparent mode. Which CLI command must the engineer execute first to perform this conversion?

Options:
A.

no configure manager

B.

no configure firewall routed

C.

configure manager delete

D.

configure firewall transparent

Questions 53

Which Cisco Secure Firewall Threat Defense interface mode must be deployed when implementing an IPS that uses a SPAN port for traffic monitoring?

Options:
A.

Routed

B.

Passive

C.

Transparent

D.

Inline

Questions 54

An engineermustconfigure a Cisco FMC dashboard in a multidomain deployment Which action must the engineer take to edit a report template from an ancestor domain?

Options:
A.

Add it as a separate widget.

B.

Copy it to the current domain

C.

Assign themselves ownership of it

D.

Change the document attributes.

Questions 55

A network administrator is implementing an active/passive high availability Cisco FTD pair.

When adding the high availability pair, the administrator cannot select the secondary peer.

What is the cause?

Options:
A.

The second Cisco FTD is not the same model as the primary Cisco FTD.

B.

An high availability license must be added to the Cisco FMC before adding the high availability pair.

C.

The failover link must be defined on each Cisco FTD before adding the high availability pair.

D.

Both Cisco FTD devices are not at the same software Version

Questions 56

A network administrator registered a new FTD to an existing FMC. The administrator cannot place the FTD in transparent mode. Which action enables transparent mode?

Options:
A.

Add a Bridge Group Interface to the FTD before transparent mode is configured.

B.

Dereglster the FTD device from FMC and configure transparent mode via the CLI.

C.

Obtain an FTD model that supports transparent mode.

D.

Assign an IP address to two physical interfaces.

Questions 57

A financial services firm is configuring split-tunnel remote access VPN on a Cisco Secure Firewall Threat Defence managed by Cisco Secure Firewall Management Center. Only traffic to 10.0 0.0/8 and 172 16 0 0/12 must traverse the VPN tunnel Internet traffic must exit locally on the client. Internal DNS queries must traverse the VPN tunnel to the corporate DNS server at 10.1.1.53 for the domain corp.finserv.local. Cisco Secure Client is deployed on all endpoints. Which configuration must be done to accomplish the task?

Options:
A.

Implement a split-tunnel exclude list for all public address space, assign 10.1 1 53 as the primary DNS server in the group policy, and enable the Umbrella Roaming Security module to handle DNS queries for non-tunneled traffic.

B.

Configure a split-tunnel include policy scoped to 10.0.0.0/8 and 172.16.0.0/12 in the group policy, and define a split-DNS entry for corp.finserv.local so Secure Client routes matching DNS queries through the tunnel to 10.1.1.53.

C.

Enable full-tunnel mode in the group policy and apply an ACL permitting only RFC-1918 traffic into the tunnel, then assign 10.1.1.53 as the primary DNS server and rely on the Windows DNS suffix search list to handle internal resolution.

D.

Use a network object group containing 10.0.0.0/8 and 172.16.0.0/12 as the split-tunnel include list, assign 8.8.8.8 as the primary DNS server in the group policy, and configure a conditional DNS forwarder on the client for corp finserv.local

Questions 58

How does Cisco Secure Cloud Analytics handle information about network traffic?

Options:
A.

It forwards the information to other devices without storing it.

B.

It performs behavioral analysis on events and network-flow data.

C.

It performs heuristic analysis on events and network-flow data.

D.

It stores the information in a database without performing any analysis.

Questions 59

A security engineer must configure policies tor a recently deployed Cisco FTD. The security policy for the company dictates that when five or more connections from external sources are initiated within 2 minutes, there is cause for concern. Which type of policy must be configured in Cisco FMC \z generate an alert when this condition is triggered?

Options:
A.

application detector

B.

access control

C.

intrusion

D.

correlation

Questions 60

What is a benefit of implementing Integrated Routing and Bridging (IRB) on a Cisco Secure Firewall device?

Options:
A.

Multiple physical interfaces on the device can be on the same VLAN.

B.

Uptime is increased by preventing the device from being a single point of failure.

C.

Customers with different security policies can reside on the same device.

D.

Threat information can be dynamically updated from Cisco Talos.