Weekend Special Sale 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: sale75best

Free Cisco 350-701 Practice Exam with Questions & Answers | Set: 15

Questions 211

What are two reasons for implementing a multifactor authentication solution such as Duo Security provide to an

organization? (Choose two)

Options:
A.

flexibility of different methods of 2FA such as phone callbacks, SMS passcodes, and push notifications

B.

single sign-on access to on-premises and cloud applications

C.

integration with 802.1x security using native Microsoft Windows supplicant

D.

secure access to on-premises and cloud applications

E.

identification and correction of application vulnerabilities before allowing access to resources

Cisco 350-701 Premium Access
Questions 212

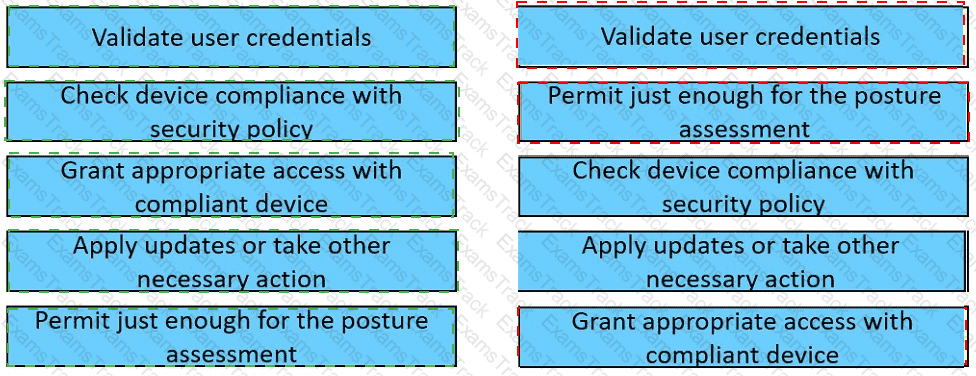
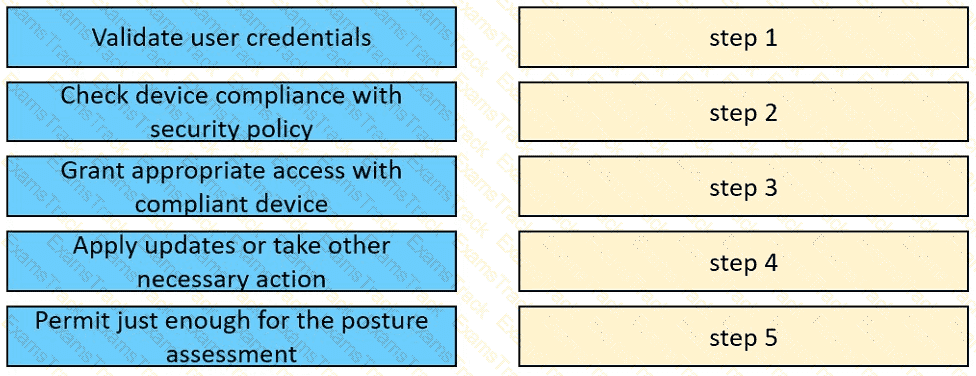
Drag and drop the posture assessment flow actions from the left into a sequence on the right.
350-701 Question 212

Options:
Questions 213

An administrator configures a new destination list in Cisco Umbrella so that the organization can block specific domains for its devices. What should be done to ensure that all subdomains of domain.com are blocked?

Options:
A.

Configure the *.com address in the block list.

B.

Configure the *.domain.com address in the block list

C.

Configure the *.domain.com address in the block list

D.

Configure the domain.com address in the block list

Questions 214

An engineer implements Cisco CloudLock to secure a Microsoft Office 365 application in the cloud. The engineer must configure protection for corporate files in case of any incidents. Which two actions must be taken to complete the implementation? (Choose two.)

Options:
A.

Expire the public share URL

B.

Send Cisco Webex message to specified users when an incident is triggered

C.

Transfer ownership of the files to a specified owner and folder

D.

Remove all users as collaborators on the files

E.

Disable the ability for commenters and viewers to download and copy the files

Questions 215

A mall provides security services to customers with a shared appliance. The mall wants separation of

management on the shared appliance. Which ASA deployment mode meets these needs?

Options:
A.

routed mode

B.

transparent mode

C.

multiple context mode

D.

multiple zone mode

Questions 216

Which protocol does the BYOD component in Cisco ISE use to obtain a unique device certificate from an internal CA?

Options:
A.

CMP

B.

SCEP

C.

SFTP

D.

OCSP

Questions 217

Which feature requires a network discovery policy on the Cisco Firepower Next Generation Intrusion Prevention

System?

Options:
A.

Security Intelligence

B.

Impact Flags

C.

Health Monitoring

D.

URL Filtering

Questions 218

An organization is trying to improve their Defense in Depth by blocking malicious destinations prior to a

connection being established. The solution must be able to block certain applications from being used within the network. Which product should be used to accomplish this goal?

Options:
A.

Cisco Firepower

B.

Cisco Umbrella

C.

ISE

D.

AMP

Questions 219

What are two rootkit types? (Choose two)

Options:
A.

registry

B.

virtual

C.

bootloader

D.

user mode

E.

buffer mode

Questions 220

A company is experiencing exfiltration of credit card numbers that are not being stored on-premise. The

company needs to be able to protect sensitive data throughout the full environment. Which tool should be used

to accomplish this goal?

Options:
A.

Security Manager

B.

Cloudlock

C.

Web Security Appliance

D.

Cisco ISE

Questions 221

Which Cisco Firewall solution requires zone definition?

Options:
A.

CBAC

B.

Cisco AMP

C.

ZBFW

D.

Cisco ASA

Questions 222

A Cisco ISE engineer configures Central Web Authentication (CWA) for wireless guest access and must have the guest endpoints redirect to the guest portal for authentication and authorization. While testing the policy, the engineer notices that the device is not redirected and instead gets full guest access. What must be done for the redirect to work?

Options:
A.

Tag the guest portal in the CWA part of the Common Tasks section of the authorization profile for the authorization policy line that the unauthenticated devices hit.

B.

Use the track movement option within the authorization profile for the authorization policy line that the unauthenticated devices hit.

C.

Create an advanced attribute setting of Cisco:cisco-gateway-id=guest within the authorization profile for the authorization policy line that the unauthenticated devices hit.

D.

Add the DACL name for the Airespace ACL configured on the WLC in the Common Tasks section of the authorization profile for the authorization policy line that the unauthenticated devices hit.

Questions 223

Which option is the main function of Cisco Firepower impact flags?

Options:
A.

They alert administrators when critical events occur.

B.

They highlight known and suspected malicious IP addresses in reports.

C.

They correlate data about intrusions and vulnerability.

D.

They identify data that the ASA sends to the Firepower module.

Questions 224

Which Secure Email Gateway implementation method segregates inbound and outbound email?

Options:
A.

Pair of logical listeners on a single physical interface with two unique logical IPv4 addresses and one IPv6 address

B.

One listener on one logical IPv4 address on a single logical interface

C.

Pair of logical IPv4 listeners and a pair of IPv6 listeners on two physically separate interfaces

D.

One listener on a single physical interface

Questions 225

What is a difference between weak passwords and missing encryption?

Options:
A.

Weak passwords allow programs to be renamed, and missing encryption hides .exe extensions.

B.

Weak passwords cause programs to crash, and missing encryption sends data to a memory location.

C.

Weak passwords consume bandwidth, and missing encryption allows user information to be hijacked.

D.

Weak passwords are guessed easily, and missing encryption allows information to be decrypted.

Cisco Related Exams

How to pass Cisco 300-710 - Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Exam
How to pass Cisco 300-715 - Implementing and Configuring Cisco Identity Services Engine (SISE) v1.1 (300-715 SISE) Exam
How to pass Cisco 300-720 - Securing Email with Cisco Email Security Appliance (300-720 SESA) Exam
How to pass Cisco 300-725 - Securing the Web with Cisco Web Security Appliance (300-725 SWSA) Exam
How to pass Cisco 300-730 - Implementing Secure Solutions with Virtual Private Networks (SVPN) Exam
How to pass Cisco 300-735 - Automating and Programming Cisco Security Solutions (300-735 SAUTO) Exam
How to pass Cisco 300-740 - Designing and Implementing Secure Cloud Access for Users and Endpoints Exam
How to pass Cisco 300-745 - Designing Cisco Security Infrastructure Exam

Cisco Free Exams

Cisco Free Exams
Examstrack offers free Cisco exam materials and practice tests to aid your Cisco certification journey.