Weekend Special Sale 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: sale75best

Free Cisco 350-701 Practice Exam with Questions & Answers | Set: 11

Questions 151

Which proxy mode must be used on Cisco WSA to redirect TCP traffic with WCCP?

Options:
A.

transparent

B.

redirection

C.

forward

D.

proxy gateway

Cisco 350-701 Premium Access
Questions 152

An organization has two machines hosting web applications. Machine 1 is vulnerable to SQL injection while machine 2 is vulnerable to buffer overflows. What action would allow the attacker to gain access to machine 1 but not machine 2?

Options:
A.

sniffing the packets between the two hosts

B.

sending continuous pings

C.

overflowing the buffer’s memory

D.

inserting malicious commands into the database

Questions 153

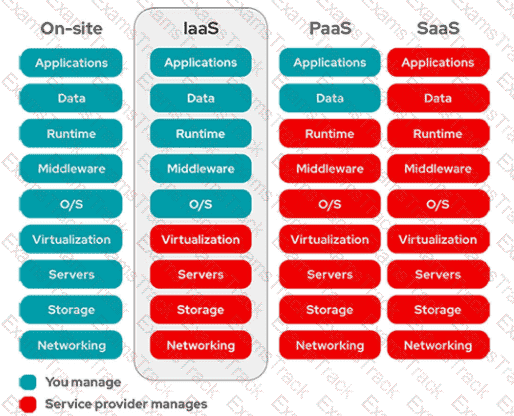
Which two aspects of the cloud PaaS model are managed by the customer but not the provider? (Choose two)

Options:
A.

virtualization

B.

middleware

C.

operating systems

D.

applications

E.

data

Questions 154

Which Cisco platform processes behavior baselines, monitors for deviations, and reviews for malicious processes in data center traffic and servers while performing software vulnerability detection?

Options:
A.

Cisco Tetration

B.

Cisco ISE

C.

Cisco AMP for Network

D.

Cisco AnyConnect

Questions 155

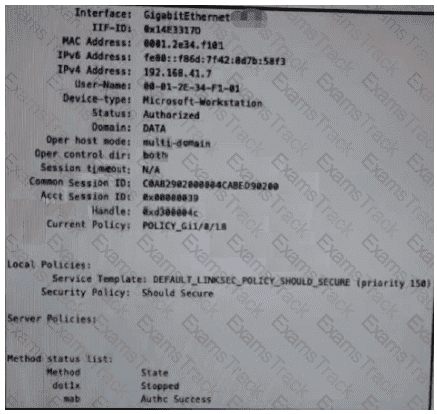
Refer to the exhibit.

350-701 Question 155

Which configuration item makes it possible to have the AAA session on the network?

Options:
A.

aaa authentication login console ise

B.

aaa authentication enable default enable

C.

aaa authorization network default group ise

D.

aaa authorization exec default ise

Questions 156

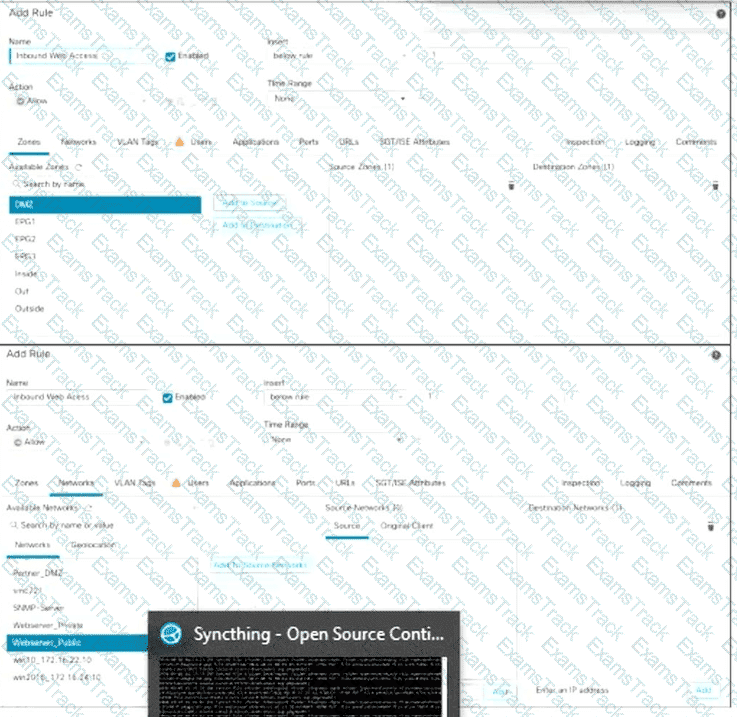
Refer to the exhibit.

350-701 Question 156

A security engineer is publishing a public web server located in the DMZ of a Cisco Secure Firewall Threat Defense device managed by Cisco Secure Firewall Management Center. The required network objects, Webserver_Private and Webserver_Public, are already defined, and an Auto NAT static rule mapping the public address to the private DMZ address is in place. The web server must be reachable from any source on the Internet. The engineer must configure a new Access Control Rule within the existing Access Control Policy. Which two configuration actions must be performed to meet the requirements? (Choose two.)

Options:
A.

Add DMZ as the Source Zone and Outside as the Destination Zone.

B.

Add Webserver_Private as the Source Network and Webserver_Public as the Destination Network.

C.

Add Any as the Source Network and Webserver_Private as the Destination Network.

D.

Add Any as the Source Network and Webserver_Public as the Destination Network.

E.

Add Outside as the Source Zone and DMZ as the Destination Zone.

Questions 157

Which action must be taken in the AMP for Endpoints console to detect specific MD5 signatures on endpoints and then quarantine the files?

Options:
A.

Configure an advanced custom detection list.

B.

Configure an IP Block & Allow custom detection list

C.

Configure an application custom detection list

D.

Configure a simple custom detection list

Questions 158

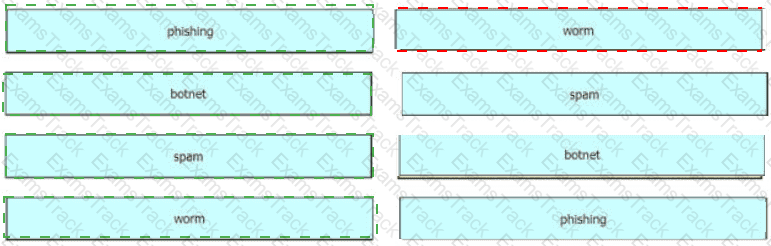
Drag and drop the common security threats from the left onto the definitions on the right.
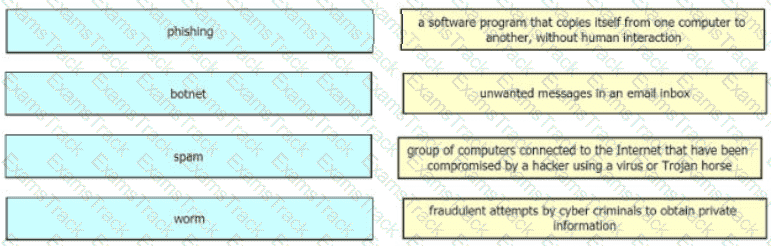
350-701 Question 158

Options:
Questions 159

Which command enables 802.1X globally on a Cisco switch?

Options:
A.

dot1x system-auth-control

B.

dot1x pae authenticator

C.

authentication port-control aut

D.

aaa new-model

Questions 160

What is an advantage of network telemetry over SNMP pulls?

Options:
A.

accuracy

B.

encapsulation

C.

security

D.

scalability

Questions 161

What is an attribute of the DevSecOps process?

Options:
A.

mandated security controls and check lists

B.

security scanning and theoretical vulnerabilities

C.

development security

D.

isolated security team

Questions 162

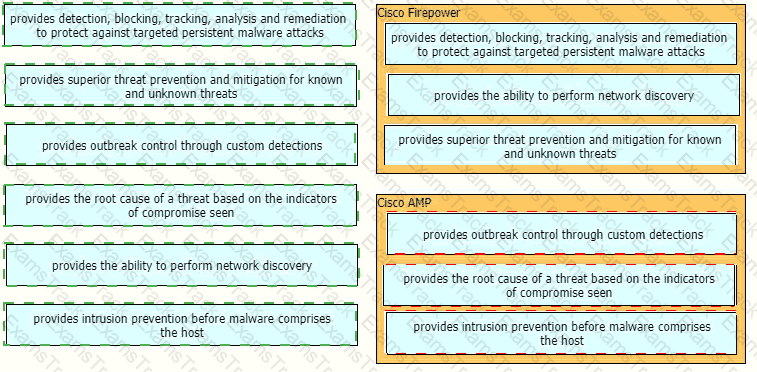
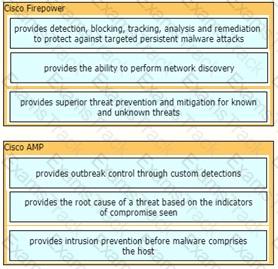
Drag and drop the capabilities of Cisco Firepower versus Cisco AMP from the left into the appropriate category on the right.
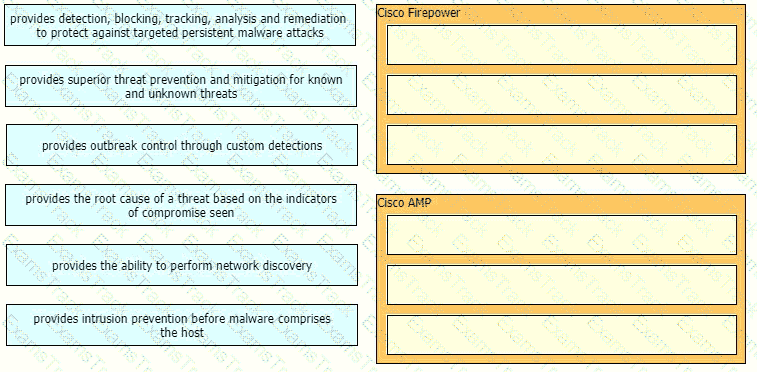
350-701 Question 162

Options:
Questions 163

What is the purpose of CA in a PKI?

Options:
A.

To issue and revoke digital certificates

B.

To validate the authenticity of a digital certificate

C.

To create the private key for a digital certificate

D.

To certify the ownership of a public key by the named subject

Questions 164

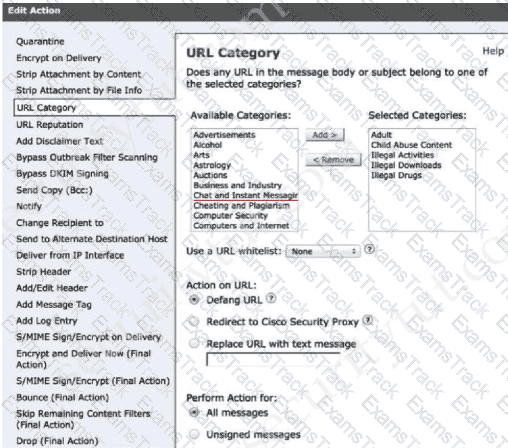
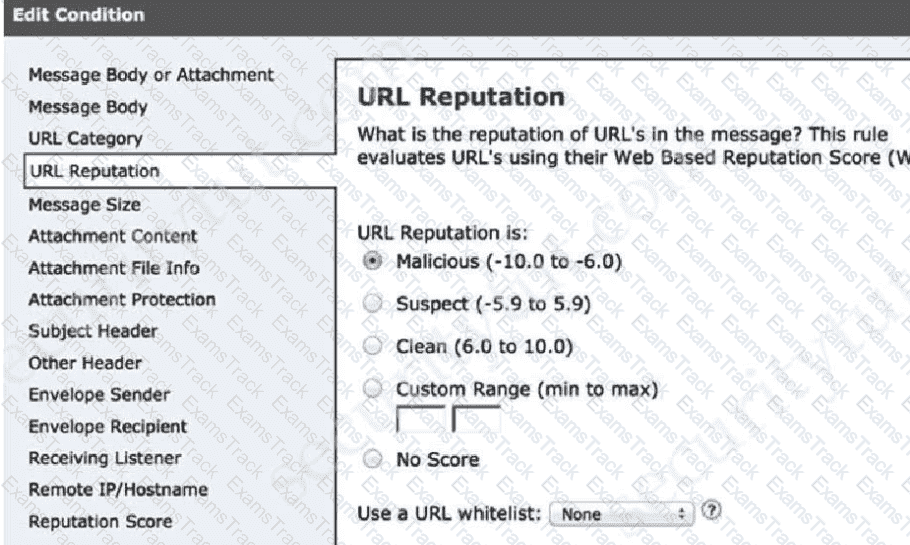
A network administrator is configuring a rule in an access control policy to block certain URLs and selects the “Chat and Instant Messaging” category. Which reputation score should be selected to accomplish this goal?

Options:
A.

1

B.

3

C.

5

D.

10

Questions 165

Which two actions does the Cisco ISE posture module provide that ensures endpoint security? (Choose two.)

Options:
A.

A centralized management solution is deployed.

B.

Patch management remediation is performed.

C.

The latest antivirus updates are applied before access is allowed.

D.

Assignments to endpoint groups are made dynamically, based on endpoint attributes.

E.

Endpoint supplicant configuration is deployed.

Cisco Related Exams

How to pass Cisco 300-710 - Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Exam
How to pass Cisco 300-715 - Implementing and Configuring Cisco Identity Services Engine (SISE) v1.1 (300-715 SISE) Exam
How to pass Cisco 300-720 - Securing Email with Cisco Email Security Appliance (300-720 SESA) Exam
How to pass Cisco 300-725 - Securing the Web with Cisco Web Security Appliance (300-725 SWSA) Exam
How to pass Cisco 300-730 - Implementing Secure Solutions with Virtual Private Networks (SVPN) Exam
How to pass Cisco 300-735 - Automating and Programming Cisco Security Solutions (300-735 SAUTO) Exam
How to pass Cisco 300-740 - Designing and Implementing Secure Cloud Access for Users and Endpoints Exam
How to pass Cisco 300-745 - Designing Cisco Security Infrastructure Exam

Cisco Free Exams

Cisco Free Exams
Examstrack offers free Cisco exam materials and practice tests to aid your Cisco certification journey.