Weekend Special Sale 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: sale75best

Free Cisco 350-701 Practice Exam with Questions & Answers | Set: 6

Questions 76

Which category includes DoS Attacks?

Options:
A.

Virus attacks

B.

Trojan attacks

C.

Flood attacks

D.

Phishing attacks

Cisco 350-701 Premium Access
Questions 77

Which open standard underpins OpenID Connect, enabling Cisco Duo to authorize application access?

Options:
A.

OAuth 2.0

B.

SCEP

C.

RSTP

D.

Kerberos

Questions 78

An engineer must deploy a Cisco Secure Web Appliance. Antimalware scanning must use the Outbreak Heuristics antimalware category on files identified as malware before performing any other processes. What must be configured on the Secure Web Appliance to meet the requirements?

Options:
A.

Sophos scanning engine

B.

Webroot scanning engine

C.

McAfee scanning engine

D.

Adaptive Scanning

Questions 79

What are two recommended approaches to stop DNS tunneling for data exfiltration and command and control call backs? (Choose two.)

Options:
A.

Use intrusion prevention system.

B.

Block all TXT DNS records.

C.

Enforce security over port 53.

D.

Use next generation firewalls.

E.

Use Cisco Umbrella.

Questions 80

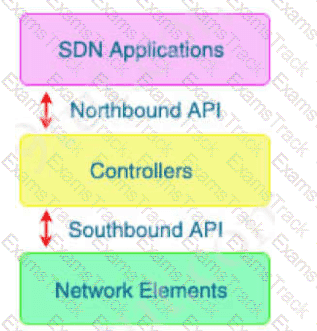
With which components does a southbound API within a software-defined network architecture communicate?

Options:
A.

controllers within the network

B.

applications

C.

appliances

D.

devices such as routers and switches

Questions 81

What is the recommendation in a zero-trust model before granting access to corporate applications and resources?

Options:
A.

To use a wired network, not wireless

B.

To use strong passwords

C.

To use multifactor authentication

D.

To disconnect from the network when inactive

Questions 82

Which kind of API that is used with Cisco DNA Center provisions SSIDs, QoS policies, and update software versions on switches?

Options:
A.

Integration

B.

Intent

C.

Event

D.

Multivendor

Questions 83

An organization wants to improve its cybersecurity processes and to add intelligence to its data The organization wants to utilize the most current intelligence data for URL filtering, reputations, and vulnerability information that can be integrated with the Cisco FTD and Cisco WSA What must be done to accomplish these objectives?

Options:
A.

Create a Cisco pxGrid connection to NIST to import this information into the security products for policy use

B.

Create an automated download of the Internet Storm Center intelligence feed into the Cisco FTD and Cisco WSA databases to tie to the dynamic access control policies.

C.

Download the threat intelligence feed from the IETF and import it into the Cisco FTD and Cisco WSA databases

D.

Configure the integrations with Talos Intelligence to take advantage of the threat intelligence that it provides.

Questions 84

A Cisco ESA network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Cisco ESA is not dropping files that have an undetermined verdict. What is causing this issue?
Options:
A.

The policy was created to send a message to quarantine instead of drop

B.

The file has a reputation score that is above the threshold

C.

The file has a reputation score that is below the threshold

D.

The policy was created to disable file analysis

Questions 85

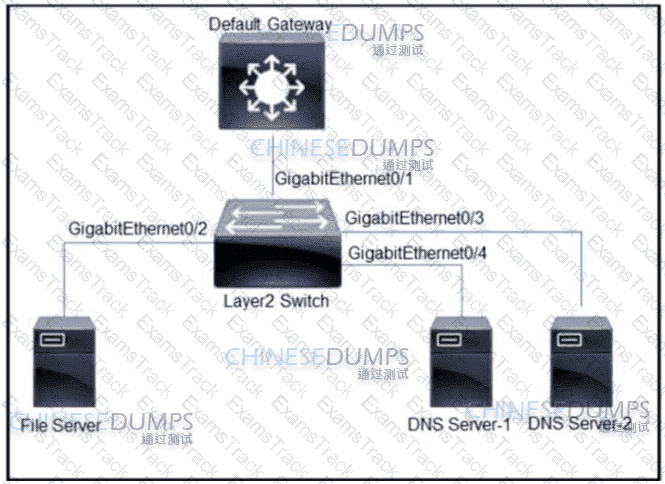
350-701 Question 85

Refer to the exhibit. All servers are in the same VLAN/Subnet. DNS Server-1 and DNS Server-2 must communicate with each other, and all servers must communicate with default gateway multilayer switch. Which type of private VLAN ports should be configured to prevent communication between DNS servers and the file server?

Options:
A.

Configure GigabitEthernet0/1 as community port, GigabitEthernet0/2 as isolated port, and GigabitEthernet0/3 and GigabitEthernet0/4 as promiscuous ports.

B.

Configure GigabitEthernet0/1 as community port, GigabitEthernet0/2 as promiscuous port, Gigabit Ethernet0/3 and GigabitEthernet0/4 as isolated ports C. Configure GigabitEthernet0/1 as promiscuous port, GigabitEthernet0/2 as isolated port and GigabitEthernet0/3 and GrgabitEthernet0/4 as community ports

C.

Configure GigabitEthernet0/1 as promiscuous port, GigabitEthernet0/2 as community port, and GigabitEthernet0/3 and GrgabitEthernet0/4 as isolated ports.

Questions 86

Which technology reduces data loss by identifying sensitive information stored in public computing

environments?
Options:
A.

Cisco SDA

B.

Cisco Firepower

C.

Cisco HyperFlex

D.

Cisco Cloudlock

Questions 87

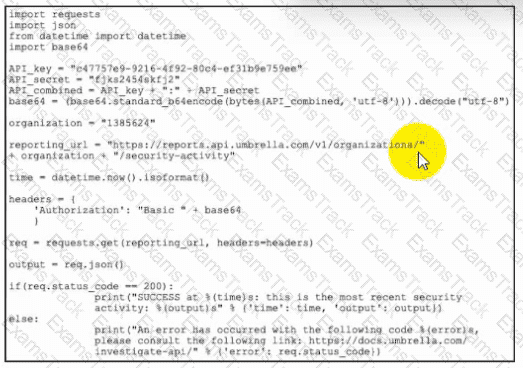
350-701 Question 87

Refer to the exhibit. Which task is the Python script performing by using the Cisco Umbrella API?

Options:
A.

Creating a list of the latest security events

B.

Copying a list of the latest security activity

C.

Retrieving a list of the latest security events

D.

Sending a list of the latest security activity

Questions 88

Which Cisco security solution secures public, private, hybrid, and community clouds?

Options:
A.

Cisco ISE

B.

Cisco ASAv

C.

Cisco Cloudlock

D.

Cisco pxGrid

Questions 89

What is a description of microsegmentation?

Options:
A.

Environments apply a zero-trust model and specify how applications on different servers or containers can communicate

B.

Environments deploy a container orchestration platform, such as Kubernetes, to manage the application delivery

C.

Environments implement private VLAN segmentation to group servers with similar applications.

D.

Environments deploy centrally managed host-based firewall rules on each server or container

Questions 90

An organization uses Cisco FMC to centrally manage multiple Cisco FTD devices. The default management

port conflicts with other communications on the network and must be changed. What must be done to ensure

that all devices can communicate together?

Options:
A.

Manually change the management port on Cisco FMC and all managed Cisco FTD devices

B.

Set the tunnel to go through the Cisco FTD

C.

Change the management port on Cisco FMC so that it pushes the change to all managed Cisco FTDdevices

D.

Set the tunnel port to 8305

Cisco Related Exams

How to pass Cisco 300-710 - Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Exam
How to pass Cisco 300-715 - Implementing and Configuring Cisco Identity Services Engine (SISE) v1.1 (300-715 SISE) Exam
How to pass Cisco 300-720 - Securing Email with Cisco Email Security Appliance (300-720 SESA) Exam
How to pass Cisco 300-725 - Securing the Web with Cisco Web Security Appliance (300-725 SWSA) Exam
How to pass Cisco 300-730 - Implementing Secure Solutions with Virtual Private Networks (SVPN) Exam
How to pass Cisco 300-735 - Automating and Programming Cisco Security Solutions (300-735 SAUTO) Exam
How to pass Cisco 300-740 - Designing and Implementing Secure Cloud Access for Users and Endpoints Exam
How to pass Cisco 300-745 - Designing Cisco Security Infrastructure Exam

Cisco Free Exams

Cisco Free Exams
Examstrack offers free Cisco exam materials and practice tests to aid your Cisco certification journey.