examstrack logo

Refer to the exhibit.
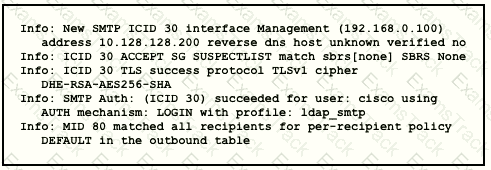
Which type of authentication is in use?
A security policy administrator configures a Cisco Secure Access SIA DNS policy to block all social media categories for the Marketing Active Directory group. While testing from one of the user machines, access to the domain https://socialmediaexample.org is allowed. When searching for this domain in User Activity Search, no queries for that specific domain are returned. Consider these facts:
The test user is part of the Marketing Active Directory group.
The domain socialmediaexample.org belongs to the social media category.
The user is configured with the Umbrella Roaming Client for DNS redirection.
All other social media websites are properly blocked for the same user and match the correct policy.
Which configuration must the administrator implement in Cisco Secure Access to meet the requirement?
A facilities team is onboarding a fleet of badge readers and IP cameras through MAB authentication on Cisco Catalyst access switches integrated with Cisco ISE. After Cisco ISE profiles each endpoint, an authorization policy must dynamically move the device into a dedicated IoT VLAN that differs from the access VLAN statically defined on the port. The endpoints lack a supplicant and cannot automatically renew their DHCP addresses. The network engineer requires Cisco ISE to issue a Change of Authorization that forces each endpoint to re-establish connectivity and request a fresh DHCP lease under the new authorization policy. Which configuration action must be performed on Cisco ISE to meet the requirement?
Which two endpoint measures are used to minimize the chances of falling victim to phishing and social
engineering attacks? (Choose two)
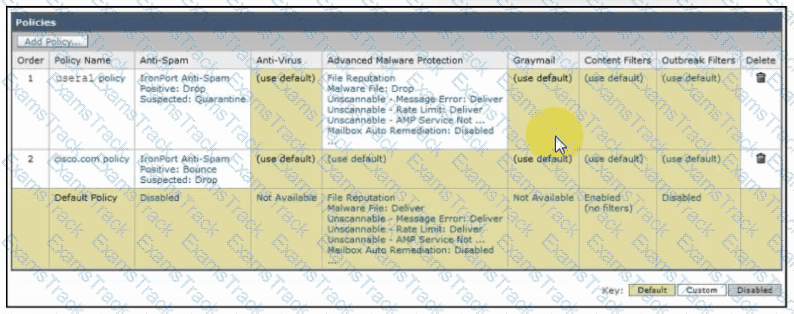
Refer to the exhibit. An engineer must configure an incoming mail policy so that each email sent from usera1@example.com to a domain of @cisco.com is scanned for antispam and advanced malware protection. All other settings will use the default behavior. What must be configured in the incoming mail policy to meet the requirements?
Which two configurations must be made on Cisco ISE and on Cisco TrustSec devices to force a session to be adjusted after a policy change is made? (Choose two)
For which type of attack is multifactor authentication an effective deterrent?
Which feature is configured for managed devices in the device platform settings of the Firepower Management
Center?
Refer to the exhibit.
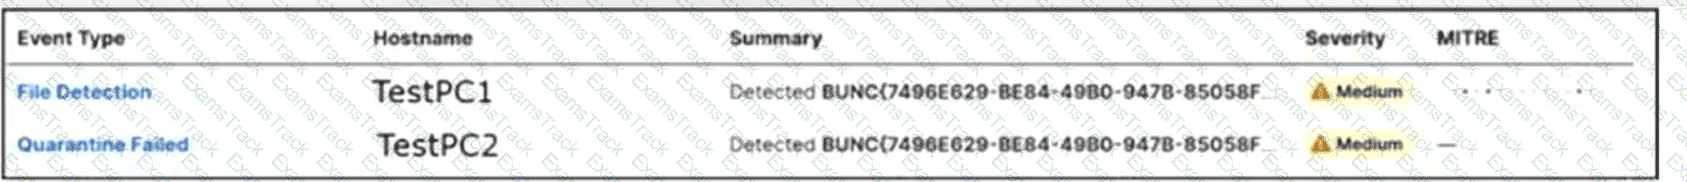
A Cisco Secure Endpoint malware event shows that a file was convicted as malicious and that its remediation status is Quarantine Failed. Before escalating the incident, the analyst must determine what can be concluded from the available event data. What is occurring based on the logs?
Which public cloud provider supports the Cisco Next Generation Firewall Virtual?
Which action controls the amount of URI text that is stored in Cisco WSA logs files?
Which mitigation strategy should be used to protect against session hijacking attacks in a cloud environment?
Refer to the exhibit.
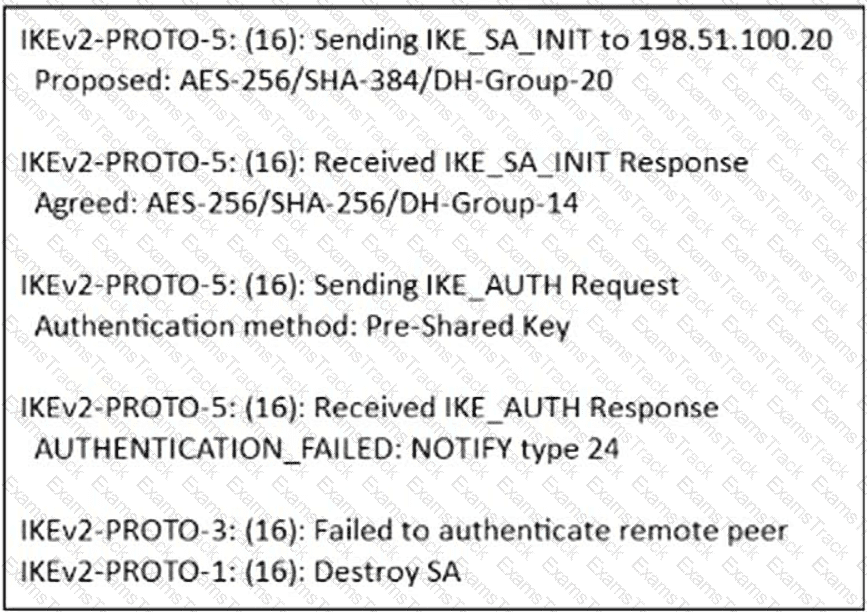
A site-to-site IKEv2 VPN between a Cisco Secure Firewall Threat Defense device with public IP address 203.0.113.10 and a third-party firewall with public IP address 198.51.100.20 is failing to establish at a logistics company. The engineer enables IKEv2 debugging on the FTD and captures the output. Which action must be performed to resolve the issue?
Which capability allows an administrator to configure forensics rules in Cisco Secure Workload?
Which system performs compliance checks and remote wiping?
|
PDF + Testing Engine
|
|---|
|
$43.75 |
|
Testing Engine
|
|---|
|
$33.75 |
|
PDF (Q&A)
|
|---|
|
$28.75 |
Cisco Free Exams |
|---|

|

Copyright © 2026 Examstrack. All Rights Reserved

TESTED 11 Oct 2026
