examstrack logo
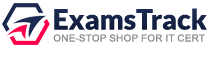
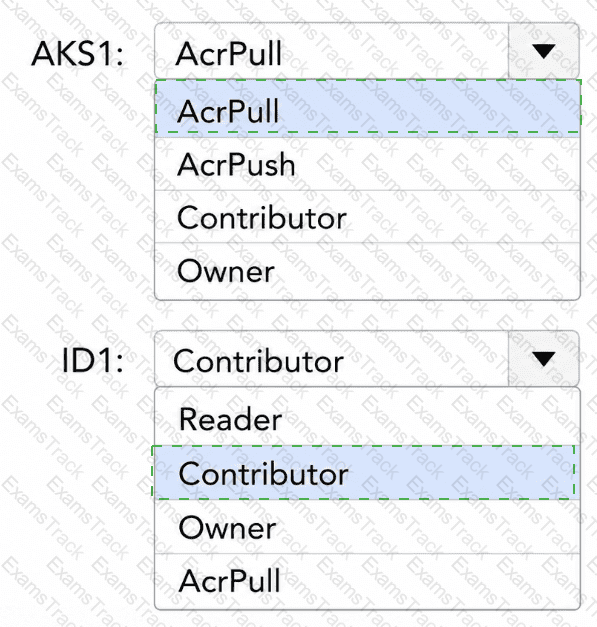
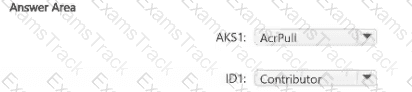
You need to configure the AKS1 and ID 1 managed identities to meet the technical requirements. The solution must follow the principle of least privilege.
Which role should you assign to each identity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution: You create an analytics rule.
Does this meet the goal?
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution: You create a playbook
Does this meet the goal?
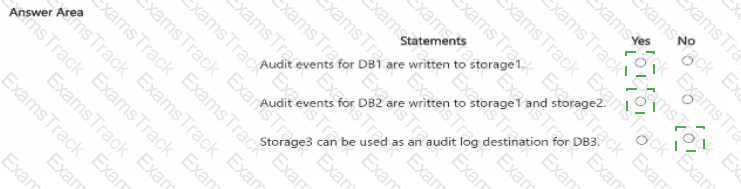
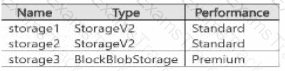
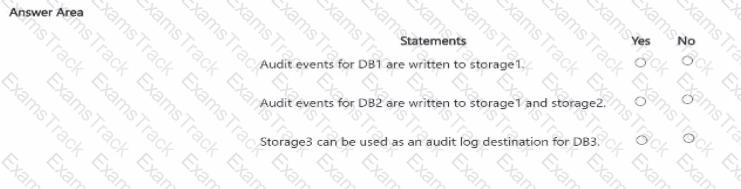
You have an Azure subscription that contains three storage accounts, an Azure SQL managed instance named SQL1, and three Azure SQL databases.
The storage accounts are configured as shown in the following table.
You plan to deploy Microsoft 365 Copilot.
You discover that Copilot can access sensitive information in your Microsoft SharePoint Online libraries.
You need to automatically identify which SharePoint Online content has been shared between all internal users.
What should you create?
You have two management groups named MG1 and MG2 that contain multiple Azure subscriptions. The subscriptions are linked to a Microsoft Entra tenant.
You have a user named User1 and a global administrator named Admin 1
You are informed that User1 created an Azure subscription named Sub1 under the MG2 management group and is the only owner of the subscription.
You need to ensure that Admin1 can remove the Owner role from User1 for Sub1.
What should you do first?
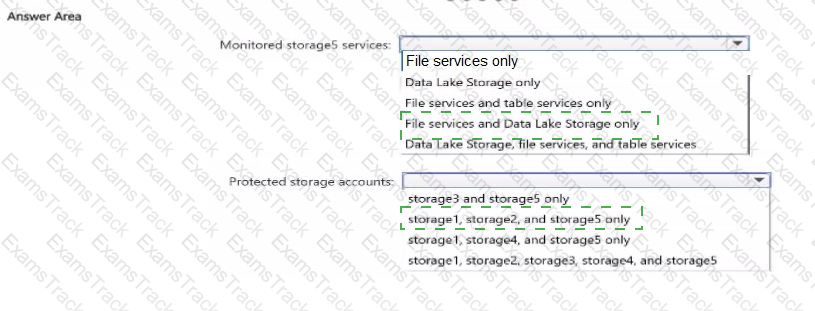
You have an Azure Subscription that contains the storage accounts shown in the following table.
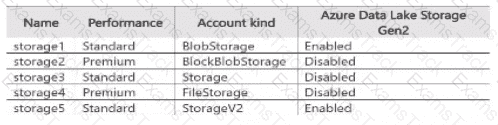
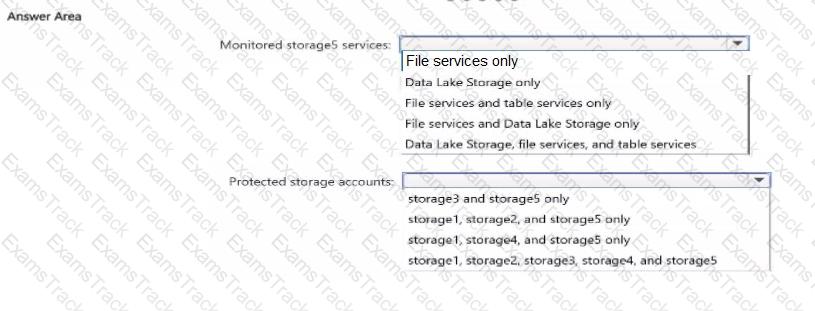
You enable Microsoft Defender for Storage.
Which storage services of storage5 are monitored by Microsoft for Storage which storage accounts are protected by.
You have an Azure SQL Database logical server named Server1 that contains a database named DB1.
You need to configure authentication for Server1 to meet the following requirements;
•SQL authentication cannot be used for any databases on Server1.
•The solution must be enforced centrally at the server level.
What should you do?
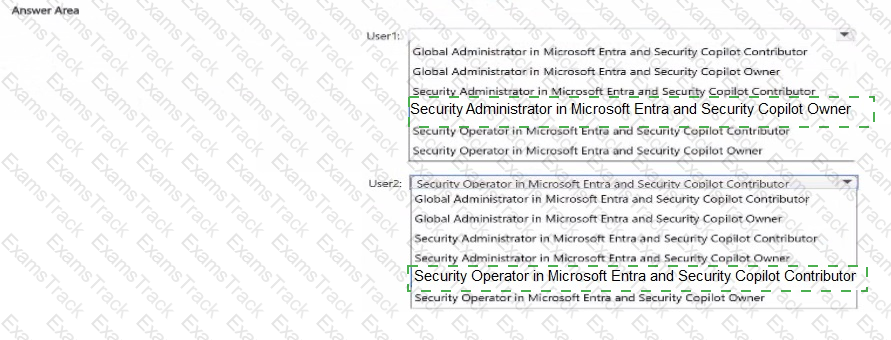
You have a Microsoft 365 tenant that uses Microsoft Security Copilot and Microsoft Defender XDR.
Access to Microsoft Defender XDR is managed by using Microsoft entra global roles.
The Phishing triage Agent is available in Microsoft Defender. The required agent prerequisites and approvals are complete
Two users will perform the following tasks:
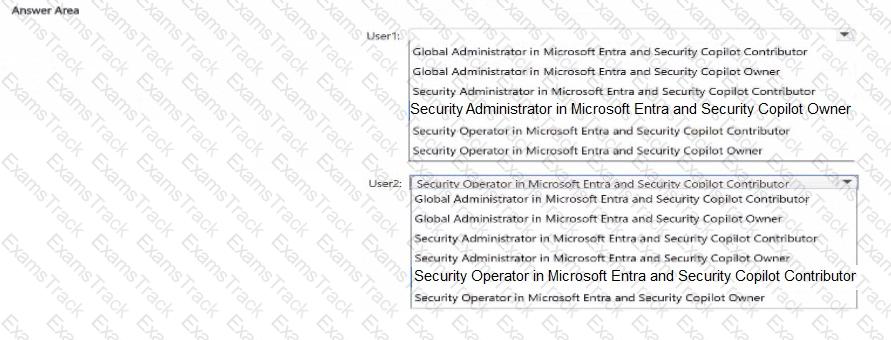
• User1 will enable and manage the Phishing Triage Agent settings.
• User2 will use Security Copilot in Microsoft Defender XDR to manage phishing incidents identified by the agent.
You need to assign the least-privileged built in Microsoft Entra role and Security Copilot role combination to each us Which roles should you assign to each user? To answer, select the appropriate options in the answer area.
You have an Azure environment.
You need to identity any Azure configurations and workloads that are non-compliant with ISO 27001:2013 standards. What should you use?
|
PDF + Testing Engine
|
|---|
|
$45 |
|
Testing Engine
|
|---|
|
$35 |
|
PDF (Q&A)
|
|---|
|
$30 |
Microsoft Free Exams |
|---|
|
Copyright © 2026 Examstrack. All Rights Reserved
TESTED 03 Nov 2026