examstrack logo
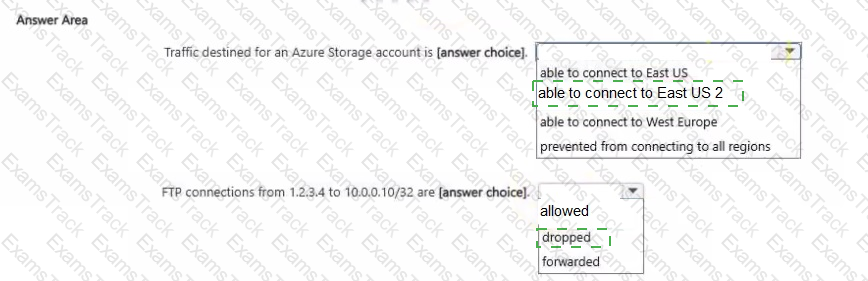
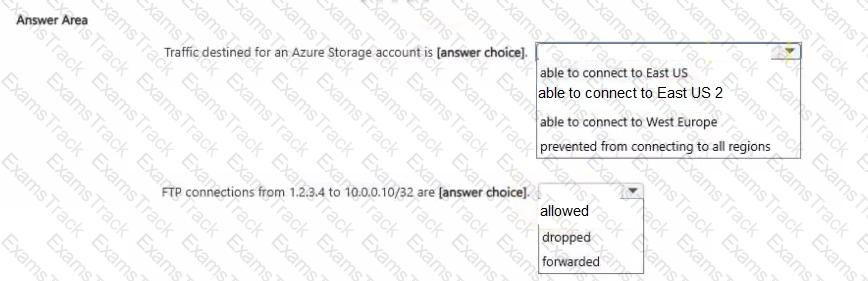
You have a network security group (NSG) bound to an Azure subnet
You run Get-AzNetworkSecurityRuleConf ig and receive the output shown in the following exhibit
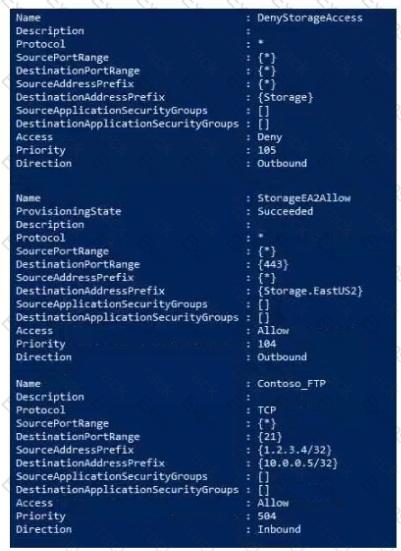
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
You have an Azure virtual network named VNet1 that contains a subnet named Subnet1.
You create a storage account named storage1.
You need to ensure that access to storage1 can be managed only by a network security group (NSG) linked to Subnet1.
What should you use?
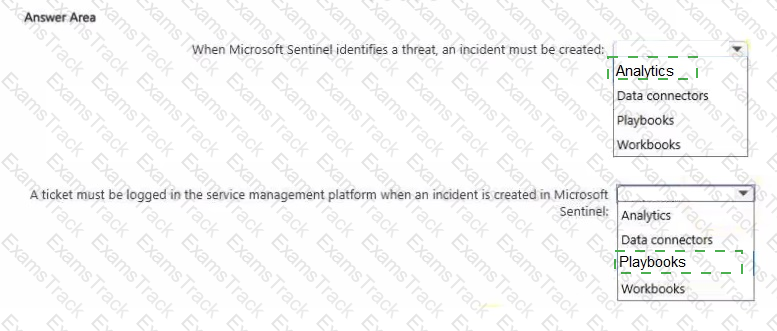
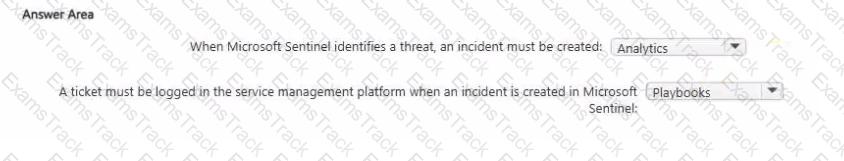
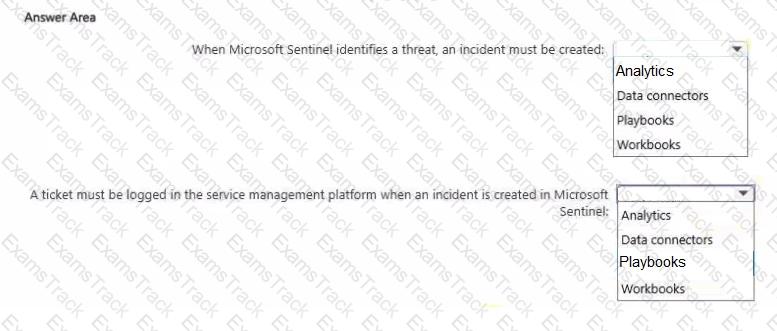
You have an Azure subscription that contains a Microsoft Sentinel workspace.
Microsoft Sentinel is configured to ingest logs from several Azure workloads. A third-party service management platform is used to manage incidents.
You need to identify which Microsoft Sentinel components to configure to meet the following requirements:
• When Microsoft Sentinel identifies a threat, an incident must be created.
• A ticket must be logged in the service management platform when an incident is created in Microsoft Sentinel.
Which component should you identify for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have an Azure Storage account named storage1 that contains Azure Files shares.
You have an application named App1 that uses a system-assigned managed identity to access the shares.
Administrators access the shares by using storage account keys.
You need to ensure that App1 access the shares without using the storage account keys.
What should you do on storage1?
HOTSPOT
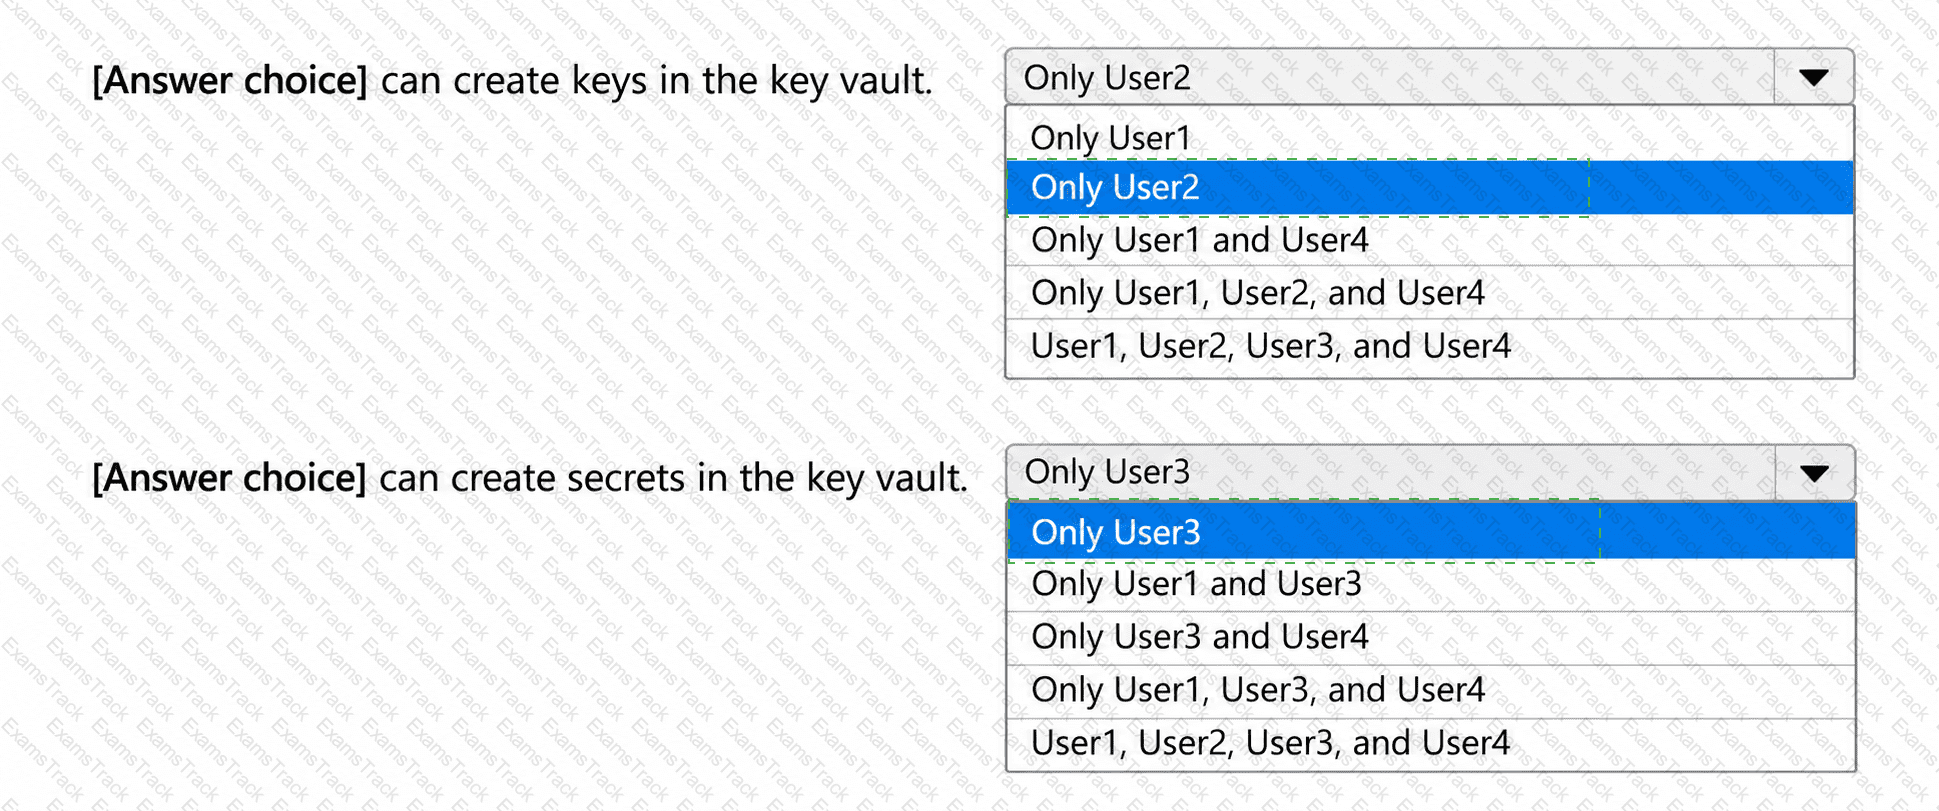
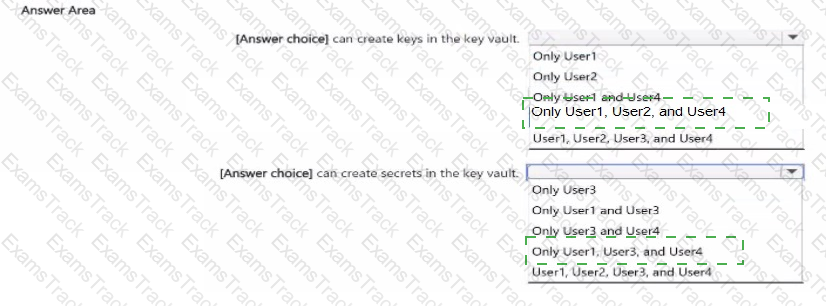
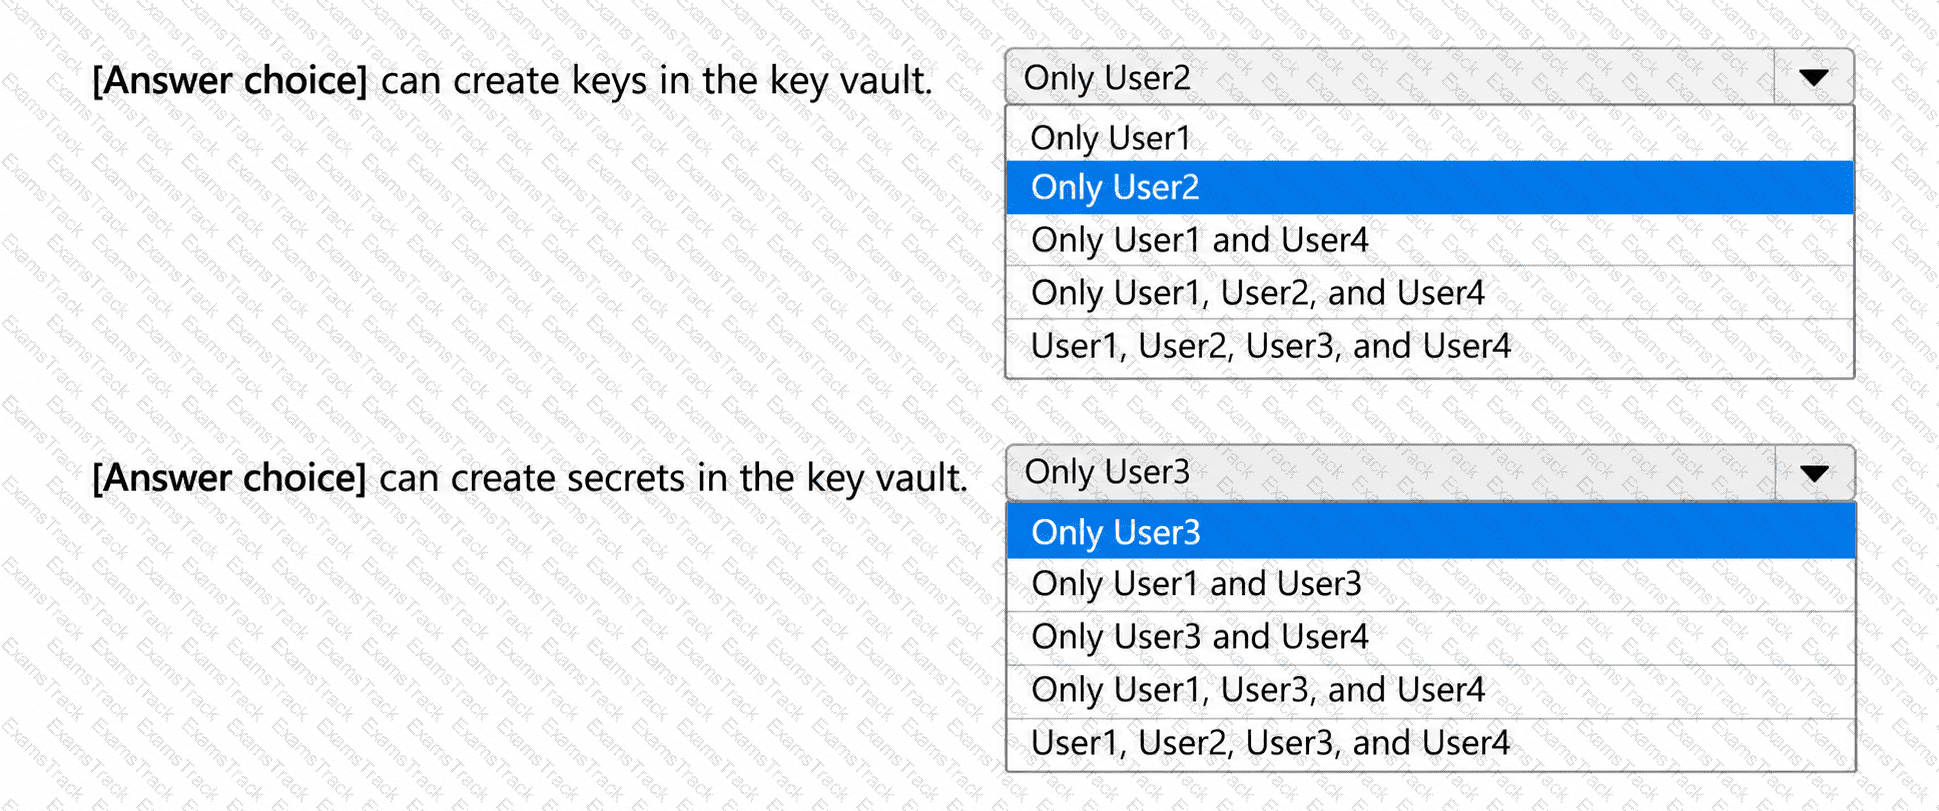
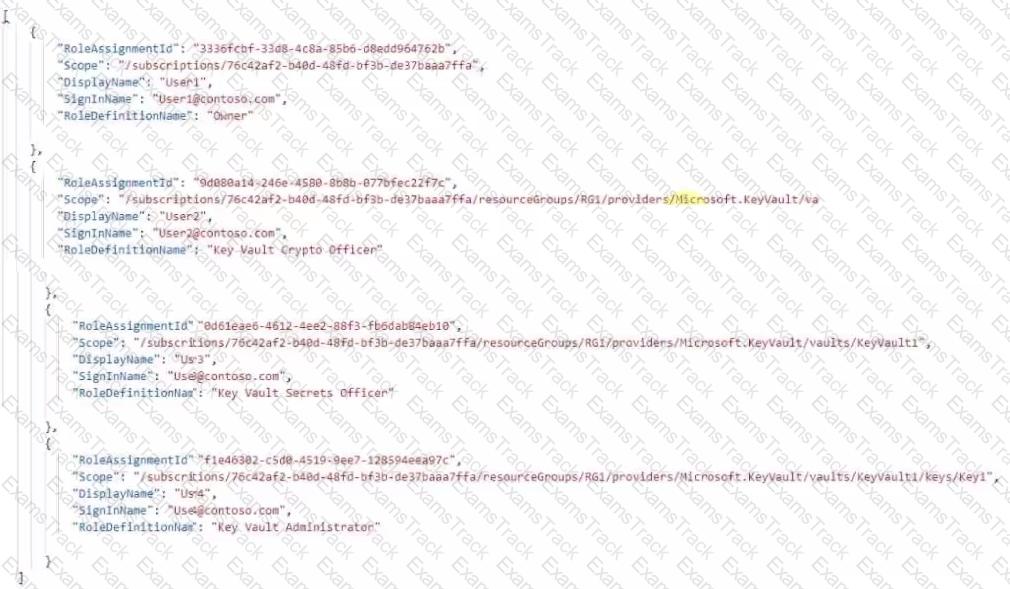
You have an Azure subscription that contains an Azure key vault named KeyVault1.
The role assignments are:
User1 → Owner, scoped to the subscription
User2 → Key Vault Crypto Officer, scoped to KeyVault1
User3 → Key Vault Secrets Officer, scoped to KeyVault1
User4 → Key Vault Administrator, scoped only to KeyVault1/keys/Key1
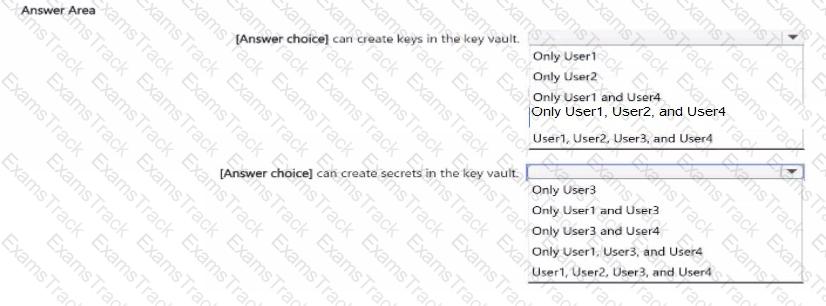
Use the drop-down menus to complete each statement.
You have a Microsoft Copilot Studio agent.
A Microsoft Power Platform administrator configures external threat detection for the agent by using a Microsoft Entra application.
You need to ensure that real-time protection is enabled during agent runtime.
What should you do in the Microsoft Defender portal?
DRAG DROP
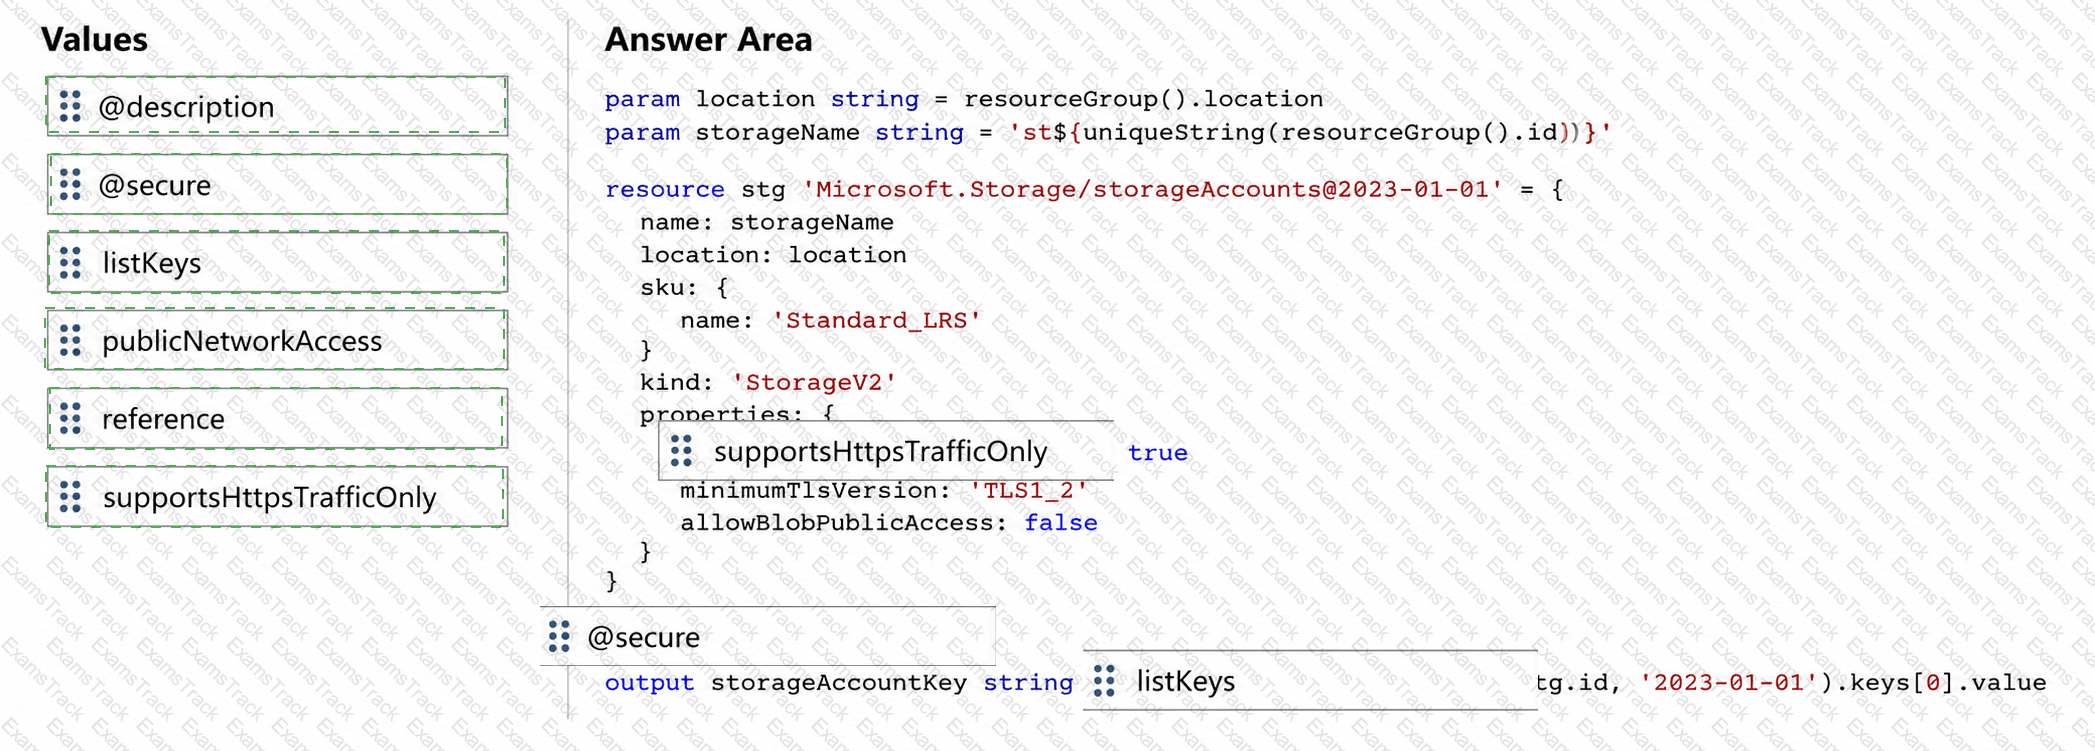
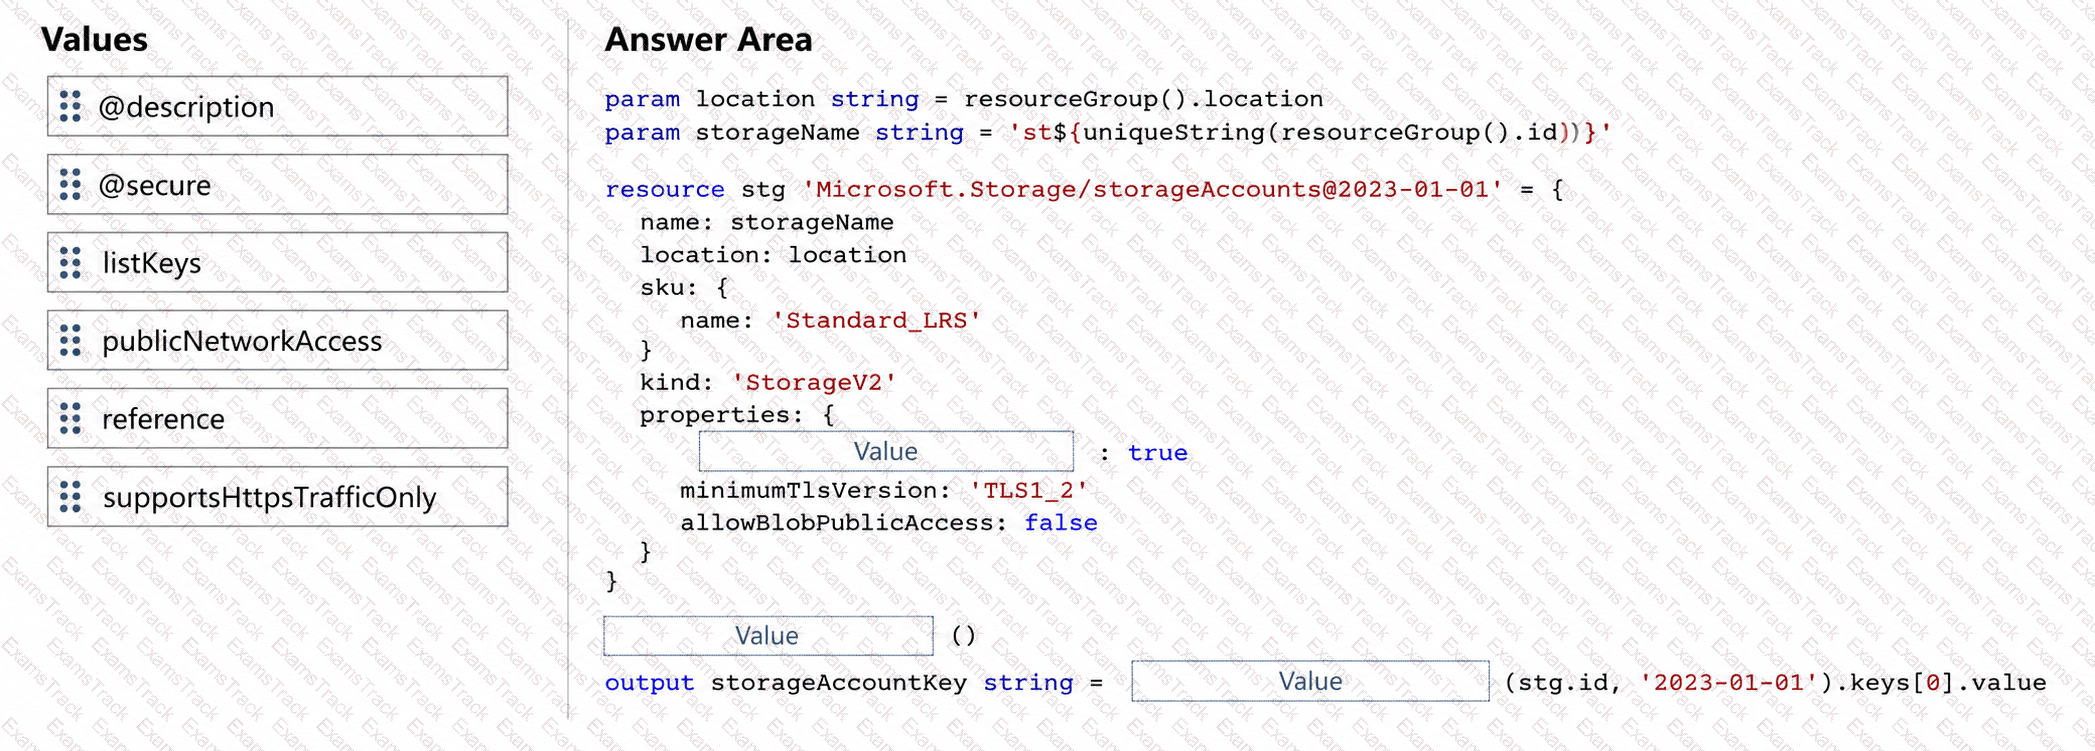
You have a Bicep file for an Azure Storage account that stores regulated data.
You need to revise the file to meet the following requirements:
Require HTTPS-only traffic.
Prevent the storage account key from being exposed in deployment outputs.
How should you complete the Bicep code?
You have an Azure subscription that contains the virtual networks shown in the following table.
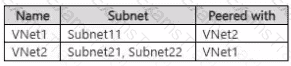
The subscription contains the virtual machines shown in the following table.
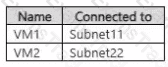
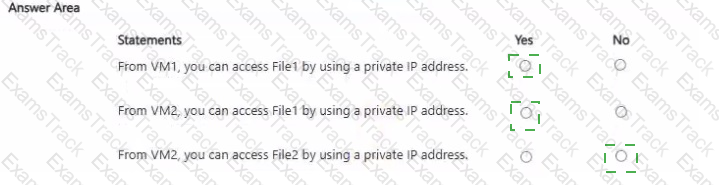
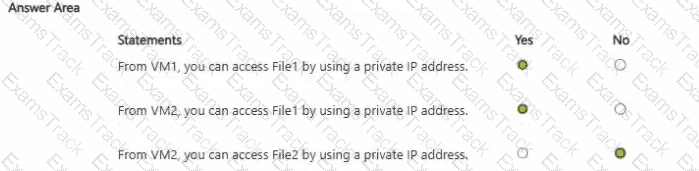
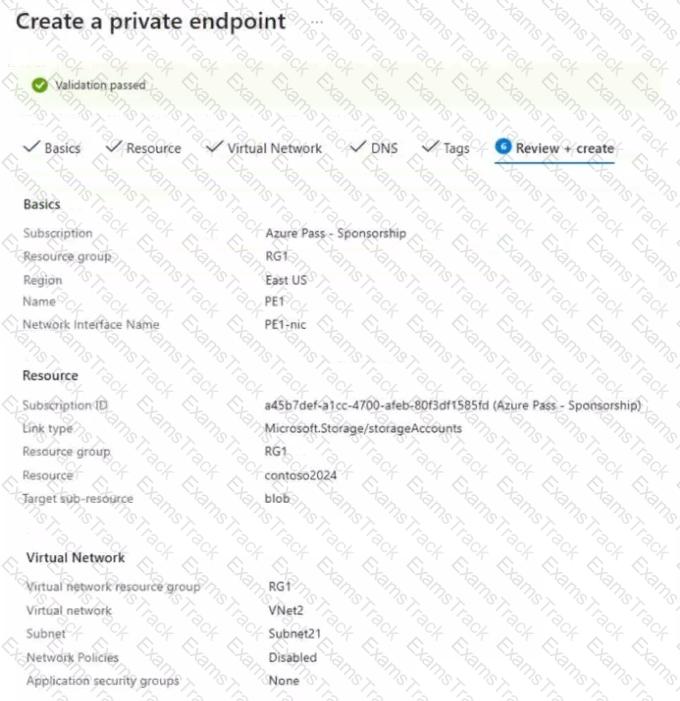
You have a storage account named contoso2024 that contains the following resources:
• A container named contained that contains a file named File1
• A file share named share1 that contains a file named File2
You create a private endpoint for contoso2024 as shown in the following exhibit.
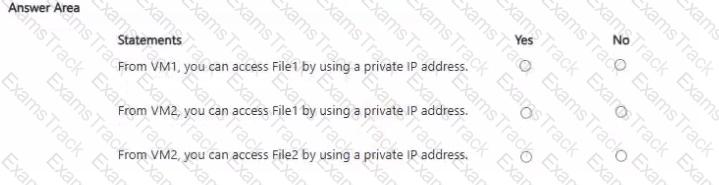
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE Each correct selection is worth one point.
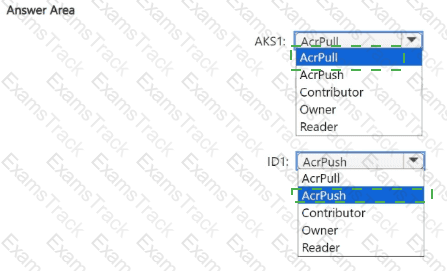
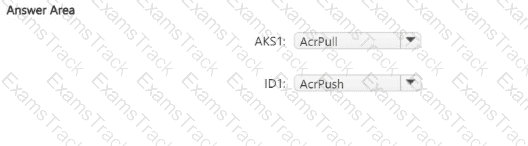
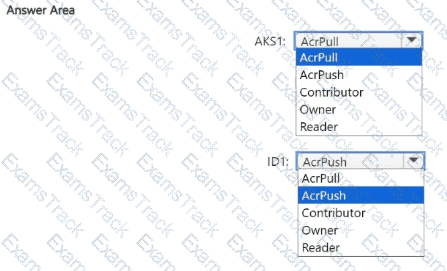
You need to configure the AKS1 and ID1 managed identities to meet the technical requirements. The solution must follow the principle of least privilege.
Which role should you assign to each identity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains an Azure Key vault. The role assignments for the vault are shown in the following.
NOTE: Each correct select is worth one point.
|
PDF + Testing Engine
|
|---|
|
$45 |
|
Testing Engine
|
|---|
|
$35 |
|
PDF (Q&A)
|
|---|
|
$30 |
Microsoft Free Exams |
|---|
|
Copyright © 2026 Examstrack. All Rights Reserved
TESTED 03 Nov 2026