examstrack logo

On a WLAN, the HSB service sets up an HSB channel between two devices that back up each other, maintains the channel status, and backs up data. Which of the following can HSB back up in real time?
Route attributes are specific descriptions of routes. BGP route attributes can be classified into four types. Which of the following are well-known discretionary attributes?
The following figure shows the WLAN topology of a large enterprise, where the direct forwarding mode is used. Which of the following is the default data forwarding path after inter-AC Layer 3 roaming of a STA?
Exhibit:
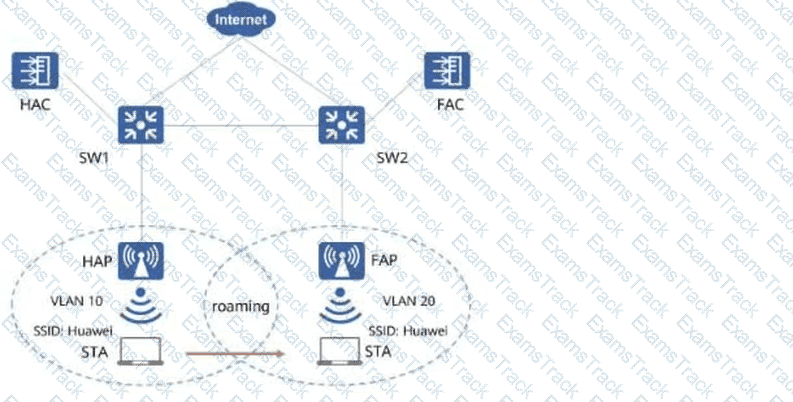
WLAN Layer 3 roaming topology with HAC, FAC, HAP, FAP, VLAN 10, and VLAN 20
A large enterprise deploys a WLAN in VRRP HSB mode to ensure WLAN reliability. Which of the following statements are false about the VRRP configuration?
Data encryption can effectively ensure VPN data security, but not all VPNs support this feature. Which of the following VPN technologies support data encryption and verification?
Route summarization can effectively reduce the number of BGP routes. However, many parameters need to be properly set when configuring BGP route summarization. Otherwise, problems such as routing loops may occur.
Which of the following statements is false about BGP route summarization?
When two BGP peers support different Hold Time, they will negotiate to support the shortest Hold Time interval they can support.
Compress the 2001:0DB8:0000:C030:0000:0000:09A0 address.
VRF, also called VPN instance, is a network virtualization technology that helps VPN technology to isolate users. In normal cases, multiple VPN instances can be created on a physical device, and each VPN instance has independent entries. Which of the following resources can be independently owned by a VPN instance?
In addition to numerous normal service packets, the CPUs of devices on a network may also receive large numbers of attack packets. To ensure that the CPUs can properly respond to normal services, the devices provide the local attack defense function.
Which of the following statements are true about this function? (Select all that apply)
|
PDF + Testing Engine
|
|---|
|
$42.5 |
|
Testing Engine
|
|---|
|
$32.5 |
|
PDF (Q&A)
|
|---|
|
$26.25 |
Huawei Free Exams |
|---|

|

Copyright © 2026 Examstrack. All Rights Reserved

TESTED 20 Nov 2026
