Halloween Special Sale 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: sale75best

Free Fortinet NSE5_FSW_AD-7.6 Practice Exam with Questions & Answers | Set: 3

Questions 21

Which statement about 802.1X security profiles using MAC-based authentication mode is true?

Options:
A.

FortiSwitch allows connectivity to all hosts connected to a port, if one host is authenticated.

B.

FortiSwitch can grant each device a different access level based on the credentials provided

C.

FortiSwitch performs faster when using this security mode on the ports.

D.

FortiSwitch must communicate with the RADIUS server to authenticate devices

Fortinet NSE5_FSW_AD-7.6 Premium Access
Questions 22

Which two statements about the FortiLink authorization process are true? (Choose two.)

Options:
A.

The administrator must manually pre-authorize FortiGate on FortiSwitch by adding the FortiGate serial number.

B.

FortiSwitch requires a reboot to complete the authorization process.

C.

A FortiLink frame is sent by FortiGate to FortiSwitch to complete the authorization.

D.

FortiLink authorization sets the FortiSwitch management mode to FortiLink.

Questions 23

Which two statements about 802.1X authentication on FortiSwitch ports are true? (Choose two.)

Options:
A.

All hosts behind an authenticated port are allowed access after a successful authentication.

B.

A security policy is used to apply 802.1 authentication on a port.

C.

A local user database must be used to authenticate devices using the 802.1X authentication protocol.

D.

All devices connecting to FortiSwitch must support 802.1X authentication.

Questions 24

Refer to the diagnostic output:

What makes the use of the sniffer command on the FortiSwitch CLI unreliable on__port__23?

Options:
A.

The types of packets captured is limited.

B.

Just the port egress payloads are printed on CLI.

C.

Only untagged VLAN traffic can be captured.

D.

The switch port might be used as a trunk member

Questions 25

(Full question statement start from here)

Refer to the exhibit.
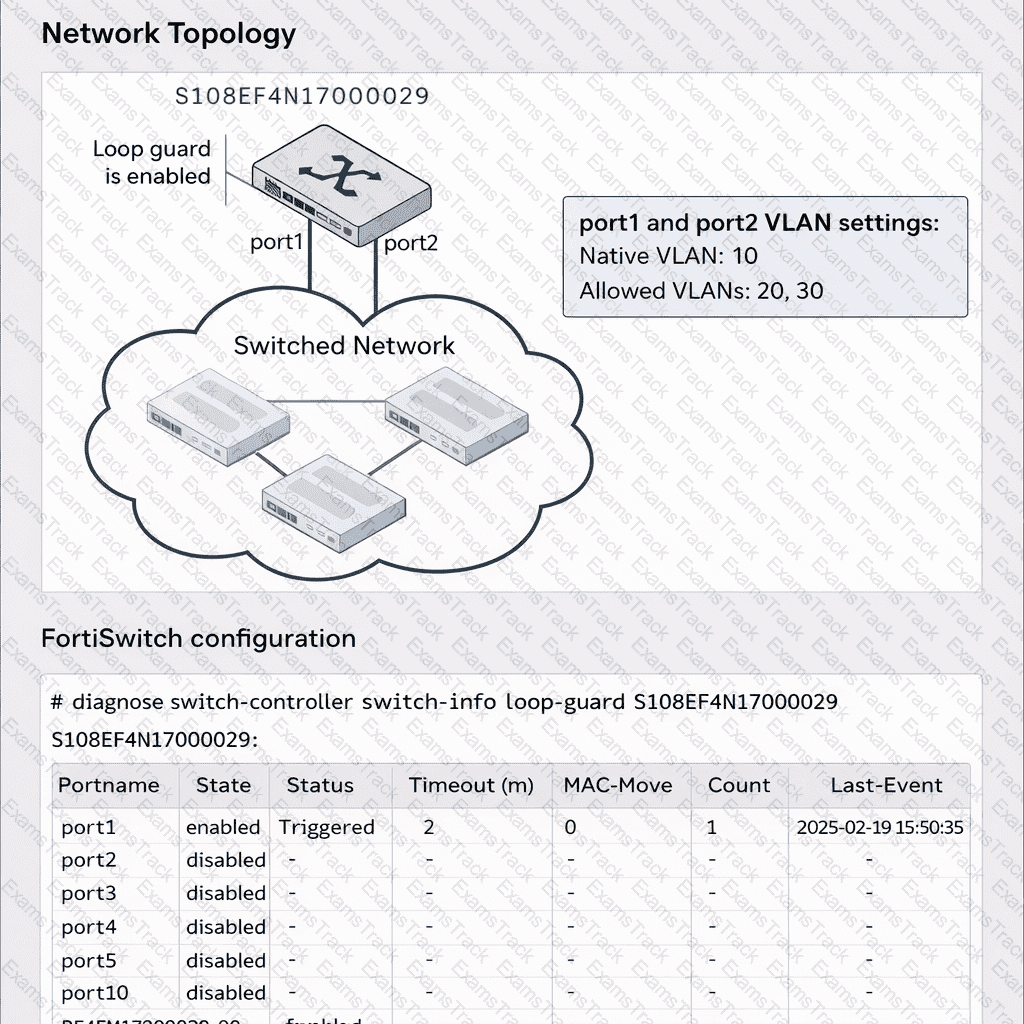
NSE5_FSW_AD-7.6 Question 25

You run the command diagnose switch-controller switch-info loopguard access-1 and see that theMAC-Movecolumn displays a value of0forport1.

What does this indicate? (Choose one answer)

Options:
A.

Loop guard is disabled on port1.

B.

Port1 is not being monitored by loop guard.

C.

The MAC move feature is not enabled.

D.

Port1 will shut down if a loop occurs on any VLAN.

Questions 26

(Full question statement start from here)

How does FortiSwitch determine the route for traffic traversing its interfaces? (Choose one answer)

Options:
A.

Hardware-based routing on FortiSwitch is handled by the CPU.

B.

ASIC hardware routing can handle only dynamic routing, if supported.

C.

FortiSwitch looks up the hardware routing table and then the forwarding information base (FIB).

D.

FortiSwitch forwards all traffic to FortiGate for routing decisions.

Questions 27

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 27

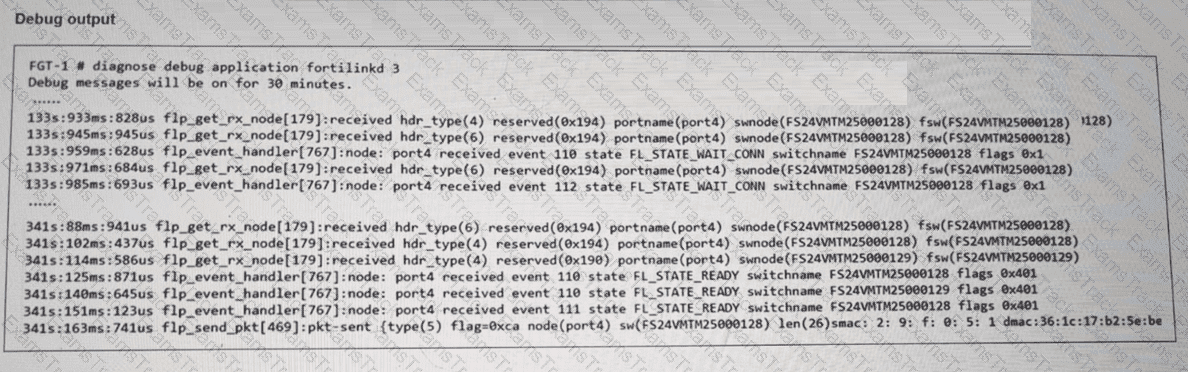
You have just authorized a new FortiSwitch on your FortiGate, and it appears online in the GUI. To verify that FortiLink connectivity is healthy, what should you check next? (Choose one answer)

Options:
A.

Check that the switch automatically disables all unused ports.

B.

Look for FortiLink heartbeat messages sent from FortiSwitch to FortiGate every few seconds and confirm FortiGate acknowledges them.

C.

Verify that FortiGate has pushed a new firmware image to FortiSwitch immediately.

D.

Ensure the FortiSwitch is automatically sending log events to FortiAnalyzer.

Questions 28

Refer to the diagnostic output:

NSE5_FSW_AD-7.6 Question 28

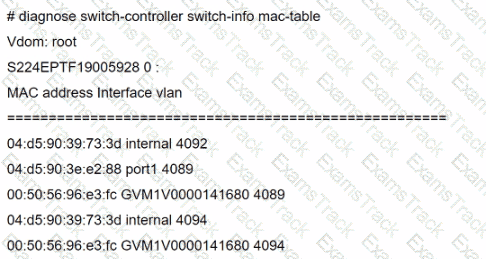
Two entries in the exhibit show that the same MAC address has been used in two different VLANs. Which MAC address is shown in the above output?

Options:
A.

It is a MAC address of FortiLink interface on FortiGate.

B.

It is a MAC address of a switch that accepts multiple VLANs.

C.

It is a MAC address of an upstream FortiSwitch.

D.

It is a MAC address of FortiGate in HA configuration.

Questions 29

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 29

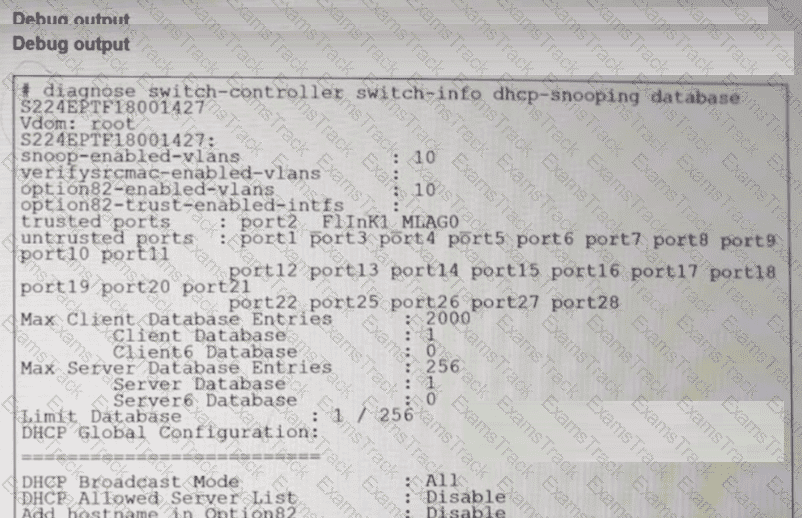
After reviewing the CLI command output, which two conclusions can you make about the Dynamic Host Configuration Protocol (DHCP) snooping configuration? (Choose two answers)

Options:
A.

DHCP snooping is disabled globally.

B.

All ports are untrusted, except port2.

C.

Option 82 is enabled on VLAN 10.

D.

DHCP broadcasts are not restricted.

Questions 30

Which packet capture method allows FortiSwitch to capture traffic on trunks and management interfaces?

Options:
A.

SPAN

B.

Sniffer profile

C.

sFlow

D.

TCP dump

Exam Code: NSE5_FSW_AD-7.6
Certification Provider: Fortinet
Exam Name: Fortinet NSE 5 - FortiSwitch 7.6 Administrator
Last Update: Oct 19, 2026
Questions: 114

Fortinet Related Exams

How to pass Fortinet NSE8_812 - Network Security Expert 8 Written Exam Exam
How to pass Fortinet FCP_FGT_AD-7.4 - FCP - FortiGate 7.4 Administrator Exam
How to pass Fortinet FCP_FGT_AD-7.6 - FortiGate 7.6 Administrator FCP_FGT_AD-7.6 Exam
How to pass Fortinet FCP_FMG_AD-7.6 - Fortinet NSE 5 - FortiManager 7.6 Administrator Exam
How to pass Fortinet FCP_FCT_AD-7.4 - Fortinet NSE 6 - FortiClient EMS 7.4 Administrator Exam
How to pass Fortinet NSE4_FGT_AD-7.6 - Fortinet NSE 4 - FortiOS 7.6 Administrator Exam
How to pass Fortinet NSE7_CDS_AR-7.6 - Fortinet NSE 7 - Public Cloud Security 7.6.4 Architect Exam
How to pass Fortinet NSE5_SSE_AD-7.6 - Fortinet NSE 5 - FortiSASE and SD-WAN 7.6 Core Administrator Exam
How to pass Fortinet NSE6_SDW_AD-7.6 - Fortinet NSE 6 - SD-WAN 7.6 Enterprise Administrator Exam
How to pass Fortinet NSE7_SSE_AD-25 - Fortinet NSE 7 - FortiSASE 25 Enterprise Administrator Exam
How to pass Fortinet NSE5_FNC_AD_7.6 - Fortinet NSE 5 - FortiNAC-F 7.6 Administrator Exam
How to pass Fortinet NSEI_OTS_AR-7.6 - Fortinet NSE I - OT Security 7.6 Architect Exam

Fortinet Free Exams

Fortinet Free Exams
Access free Fortinet exam study guides and practice tests at Examstrack. Ensure your success with top-notch preparation resources at Examstrack.