examstrack logo

Refer to the exhibit.
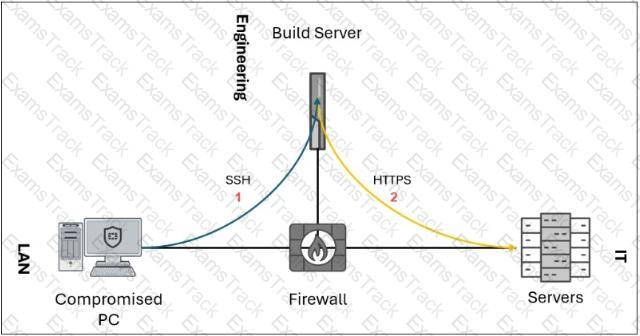
A compromised PC establishes an SSH connection to an engineering build server, which then relays HTTPS traffic to reach servers that would otherwise have blocked access from the LAN. Which technique is used for this attack?
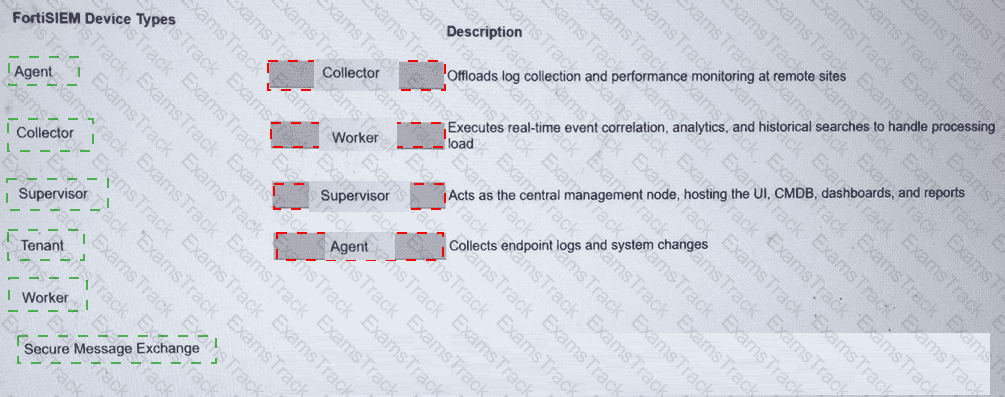
Match the FortiSIEM device type to its description. Select each FortiSIEM device type in the left column, hold and drag it to the blank space next to its corresponding description in the column on the right.
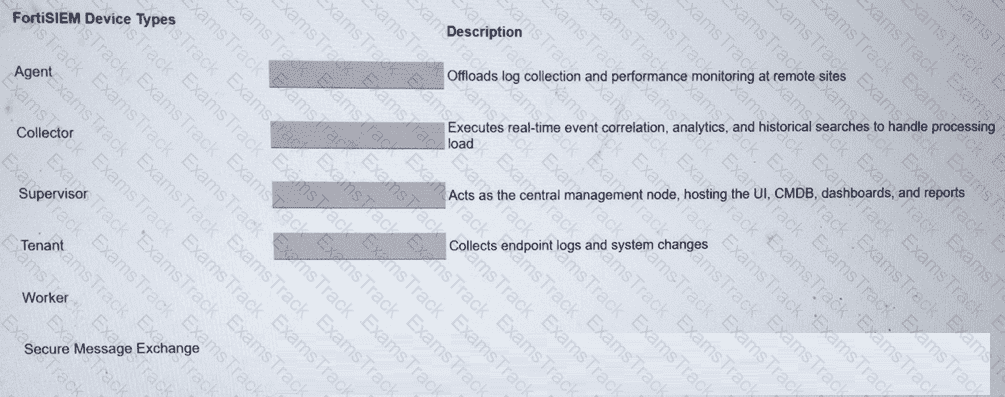
Refer to the exhibits.
You configured a custom event handler and an associated rule to generate events whenever FortiMail detects spam emails. However, you notice that the event handler is generating events for both spam emails and clean emails.
Which change must you make in the rule so that it detects only spam emails?
Exhibit:
Which observation about this FortiAnalyzer Fabric deployment architecture is true?
Which three statements accurately describe step utilities in a playbook step? (Choose three answers)
Refer to Exhibit:
A SOC analyst is designing a playbook to filter for a high severity event and attach the event information to an incident.
Which local connector action must the analyst use in this scenario?
Refer to the exhibit.
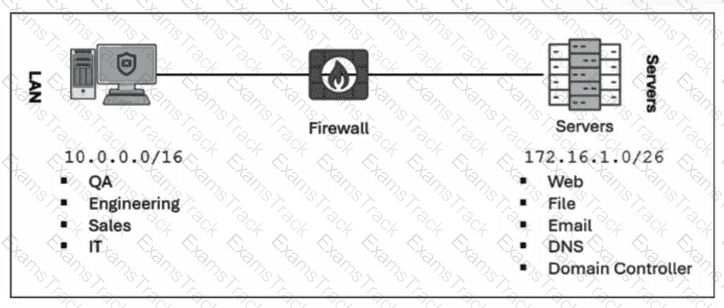
Which method most effectively reduces the attack surface of this organization? (Choose one answer)
You need to create a nested query in FortiSIEM that satisfies the following conditions:
Find all devices discovered by any FortiSIEM Windows Agent.
From those devices, identify those that have generated Windows Login Failure events.
Which two query components should be used for this nested query? Choose two answers.
You are trying to create a playbook that creates a manual task showing a list of public IPv6 addresses. You were successful in extracting all IP addresses from a previous action into a variable called ip_list, which contains both private and public IPv4 and IPv6 addresses. You must now filter the results to display only public IPv6 addresses. Which two Jinja expressions can accomplish this task? (Choose two answers)
You created a war room and want to run a connector action to look up the reputation of a domain. Then, you need to save the output for your team to review. However, there is a lot of output, and you want to limit the amount of information attached to the war room. How do you accomplish this? Choose one answer.
|
PDF + Testing Engine
|
|---|
|
$42.5 |
|
Testing Engine
|
|---|
|
$32.5 |
|
PDF (Q&A)
|
|---|
|
$26.25 |
Fortinet Free Exams |
|---|

|

Copyright © 2026 Examstrack. All Rights Reserved

TESTED 20 Nov 2026