Halloween Special Sale 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: sale75best

Free Fortinet NSE6_EDR_AD-7.0 Practice Exam with Questions & Answers

Questions 1

Which two criteria are required for integrating FortiEDR with the Fortinet Security Fabric? (Choose two answers)

Options:
A.

Central manager connected to FCS

B.

A Forensics add-on license

C.

A valid API user with access to connectors

D.

Core with core-only functionality

Fortinet NSE6_EDR_AD-7.0 Premium Access
Questions 2

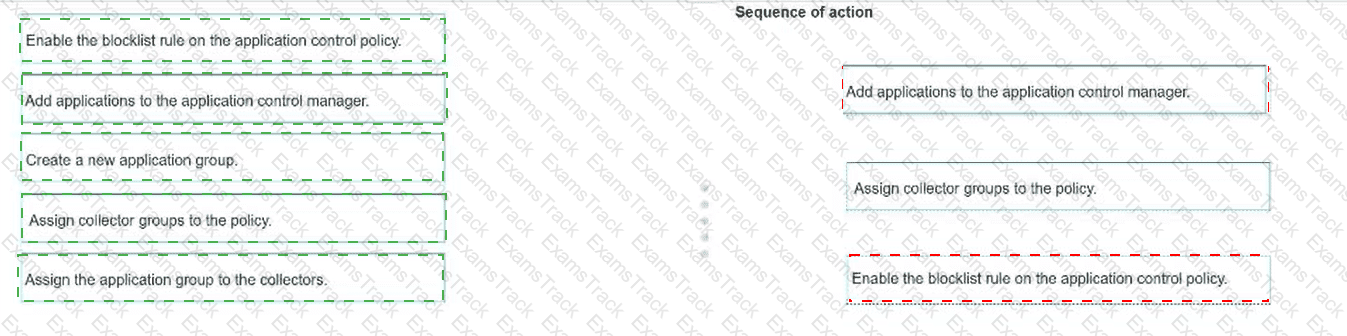
When implementing an application block policy in FortiEDR, which three actions, in order, reflect the correct operational sequence? (Choose three.)

Select an action in the left column and hold and drag it to a blank position in the column on the right. Place the three correct actions in order, starting with the first action at the top of the column. After you

place an action, you can move it again if you want to change your answer before proceeding to the next question. You must drop three actions in the work area.

Select and drag the screen divider to change the viewable area of the source and work areas.
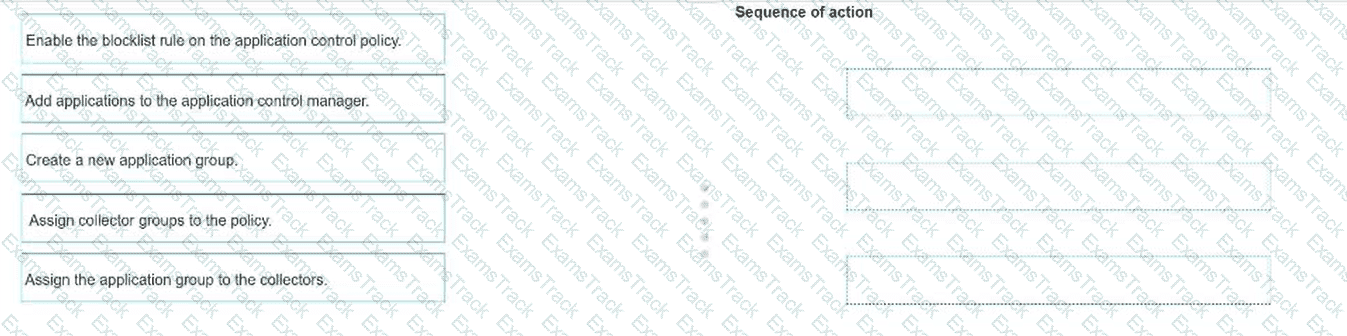
NSE6_EDR_AD-7.0 Question 2

Options:
Questions 3

You find third-party software on a user’s computer that does not appear in the application list on the communication control console. Which two statements are true about this situation? (Choose two answers)

Options:
A.

The application has not made any connection attempts.

B.

The application is blocked by the security policies.

C.

The application is ignored because its reputation score is acceptable to the security policy.

D.

The application is allowed in all communication control policies.

Questions 4

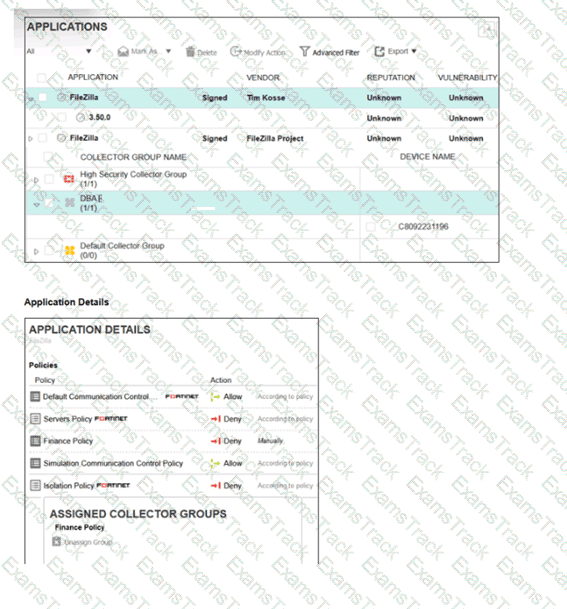
Refer to the exhibits.

NSE6_EDR_AD-7.0 Question 4

The application policy logs and application details are shown. Collector C8092231196 is a member of the Finance group. In this scenario, what must you do to block the FileZilla application? (Choose one answer)

Options:
A.

Assign the Simulation Communication Control Policy to the DBA group.

B.

Deny the application in the Finance policy.

C.

Assign the Finance policy to the DBA group.

D.

Assign the Finance policy to a broader collector group, such as the Default Collector Group.

Questions 5

A playbook is configured to block a file hash on the network through the FortiGate connector, and then isolate the device that generated the malicious hash event.

What is the expected behavior if FortiGate is unreachable?

Options:
A.

The playbook stops execution and generates a fail status.

B.

The playbook pauses execution and generates a pending status.

C.

The playbook isolates the device and generates a success status.

D.

The playbook isolates the device and generates a fail status.

Questions 6

What specific action does FortiEDR take when the Zero Trust Device Tagging playbook is activated? (Choose one answer)

Options:
A.

It removes unmanaged endpoints from FortiClient EMS.

B.

It assigns a default tag to all endpoints.

C.

It updates FortiClient EMS through an API and assigns a classification fabric tag.

D.

It disables the endpoint until a tag is assigned.

Questions 7

Which two Python commands are supported when using FortiEDR Connect to directly access a protected device shell? (Choose two answers)

Options:
A.

%upload_file

B.

%ipconfig_all

C.

%psexec

D.

%timestamp

Questions 8

A collector triggers a suspicious security incident that is initially flagged as potentially malicious. The environment is connected to the FortiEDR Cloud Service (FCS) for classification. How does FCS process the event for accurate classification? (Choose one answer)

Options:
A.

By data processing, comprehensive automated analysis, and comprehensive manual analysis

B.

By relying solely on the FortiGate firewall policies

C.

By comparing the event against only local signatures

D.

By correlating collector logs only

Questions 9

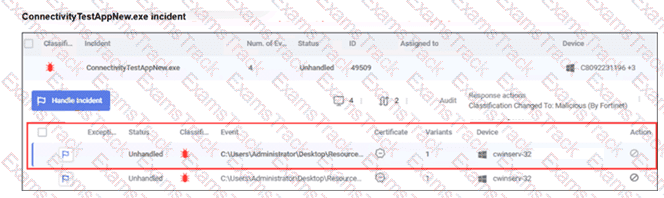
Refer to the exhibit.

NSE6_EDR_AD-7.0 Question 9

What observation can you make about the ConnectivityTestAppNew.exe incident? (Choose one answer)

Options:
A.

A rule assigned action is set to block but the policy is in simulation mode.

B.

The incident has not been handled by a console administrator.

C.

The incident was archived from the console unhandled.

D.

The incident was handled automatically by the communication control policy.

Questions 10

You are asked to create a playbook to isolate a device with a collector. Which action category does isolating a device with a collector fall under? (Choose one answer)

Options:
A.

Investigation

B.

Remediation

C.

Custom

D.

Notifications

Exam Code: NSE6_EDR_AD-7.0
Certification Provider: Fortinet
Exam Name: Fortinet NSE 6 - FortiEDR 7.0 Administrator
Last Update: Nov 1, 2026
Questions: 35
PDF + Testing Engine
$164.99
$41.25
Testing Engine
$124.99
$31.25
PDF (Q&A)
$104.99
$26.25