Halloween Special Sale 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: sale75best

Note! The FCSS_LED_AR-7.6 Exam is no longer available.

Free Fortinet FCSS_LED_AR-7.6 Practice Exam with Questions & Answers | Set: 2

Questions 11

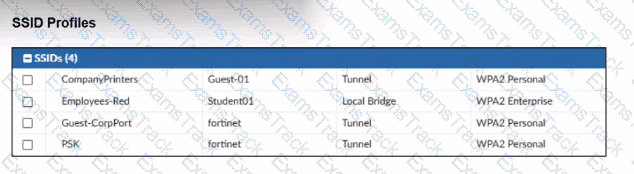
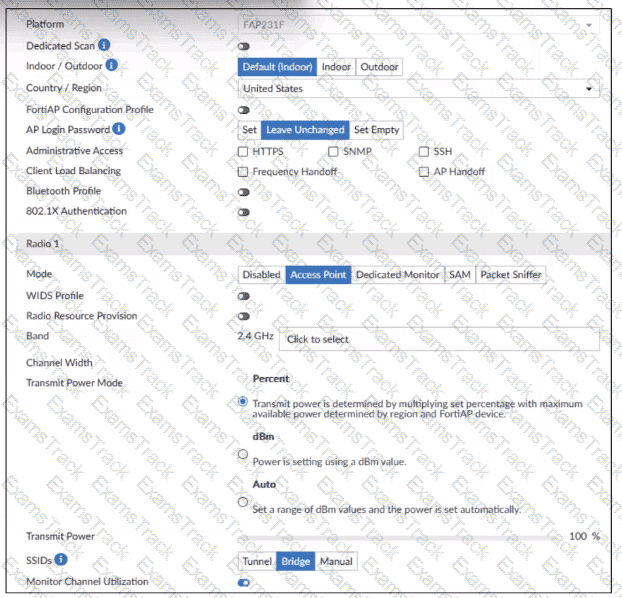
Refer to the exhibits.

FCSS_LED_AR-7.6 Question 11

FCSS_LED_AR-7.6 Question 11

A set of SSID profiles has been configured on FortiManager, and an AP profile has been assigned to a group of AP managed by FortiGate. However, none of the designated SSIDs are being broadcast by these APs.

Which configuration change is required to make the APs broadcast these SSIDs as intended?

Options:
A.

Adjust the AP profile to ensure all SSIDs are configured in a supported mode, either bridge or tunnel, but not a mix of both.

B.

Change the AP profile to use a platform that supports the configured mix of SSIDs.

C.

Choose Manual in the SSIDs setting and select the SSIDs to broadcast.

D.

Set the Transmit Power Mode to Auto.

Fortinet FCSS_LED_AR-7.6 Premium Access
Questions 12

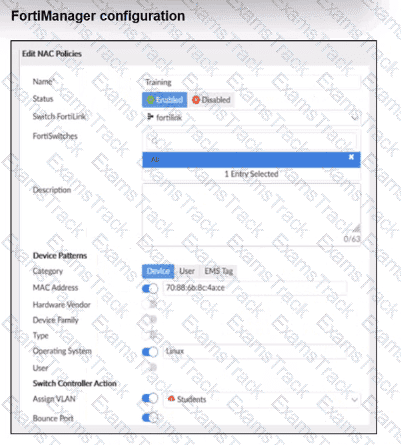
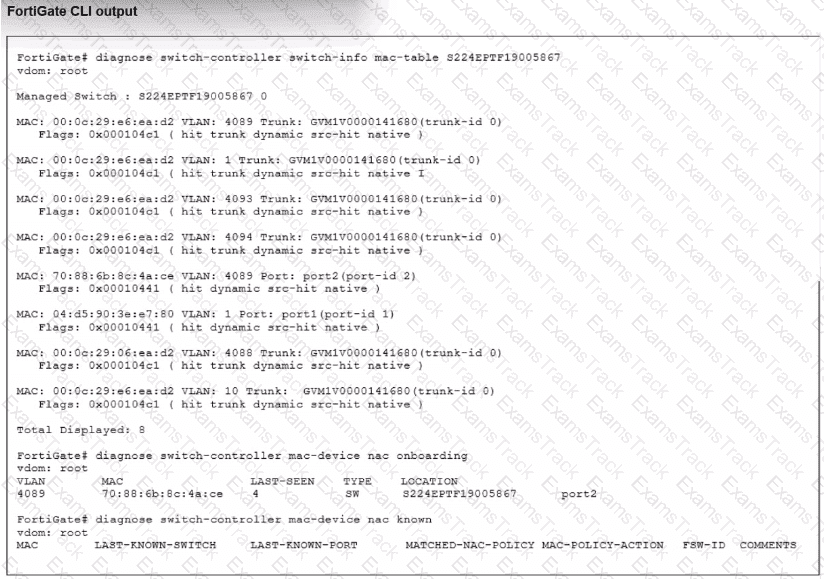
Refer to the exhibits.

FCSS_LED_AR-7.6 Question 12

FCSS_LED_AR-7.6 Question 12

Examine the FortiManager configuration and FortiGate CLI output shown in the exhibit.

The NAC feature is being tested with a device connected to port2 on managed FortiSwitch S224SPTF19005867. The NAC policy has been applied to port2, and traffic was generated from the test device. However, the traffic from the test device does not match the NAC policy and remains in the onboarding VLAN.

What are two possible reasons why the test device is not being correctly classified by the NAC policy? (Choose two.)

Options:
A.

Device detection is not enabled on VLAN 4089.

B.

The device operating system detected by FortiGate is not Linux.

C.

Management communication between FortiGate and FortiSwitch is down.

D.

The MAC address configured on the NAC policy is incorrect.

Questions 13

Which statement about generating a certificate signing request (CSR) for a CER certificate is true?

Options:
A.

Inaccurate or missing fields in the CSR will prevent the CA from validating the request, leading to the rejection of the certificate and possible delays in the deployment process.

B.

If key fields like the common name (CN) and organization (O) are incorrect, the certification authority (CA) will still issue the certificate, but it may not be trusted by certain applications or systems that rely on accurate field information for validation.

C.

CSR fields are primarily used for internal recordkeeping by the requesting organization, and only the public key in the CSR must be accurate for successful certificate signing.

D.

The fields in the CSR are primarily for documentation purposes; any missing or incorrect information will be automatically corrected by the CA during the signing process.

Questions 14

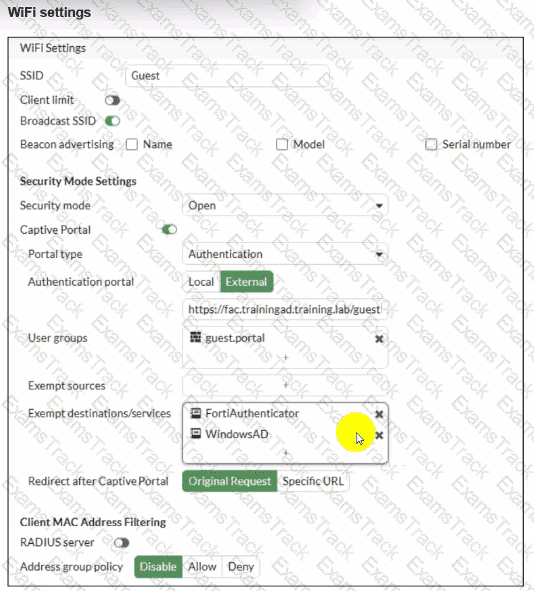
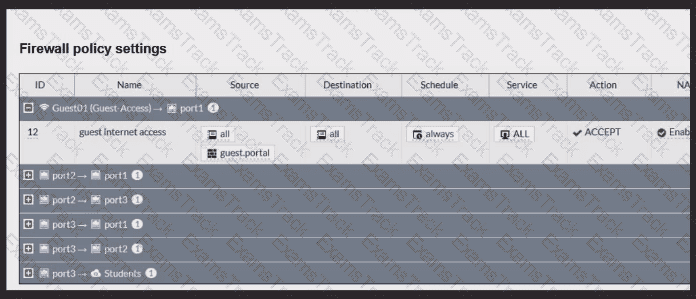
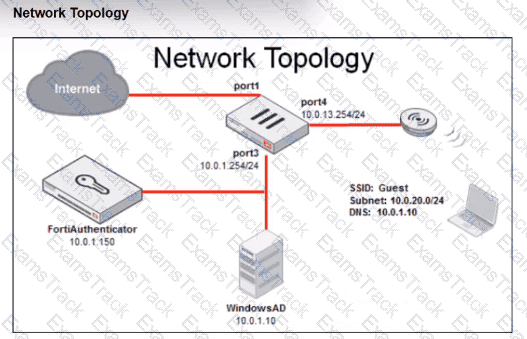
Refer to the exhibits to analyze a network topology and SSID settings.
FCSS_LED_AR-7.6 Question 14

FCSS_LED_AR-7.6 Question 14

FCSS_LED_AR-7.6 Question 14

FortiGate is configured to use an external captive portal for authentication to grant access to a wireless network. Testing detected that users attempting to access the SSID are not able to access the captive portal login page. Which configuration change should fix this issue?

Options:
A.

Change the SSID security mode to WPA2-Enterprise for authentication.

B.

Firewall policy with the ID 13 must have NAT disabled.

C.

Address objects FortiAuthenticator and WindowsAD must be included as exempt destinations/services.

D.

A firewall policy with port4 as source is missing.