examstrack logo
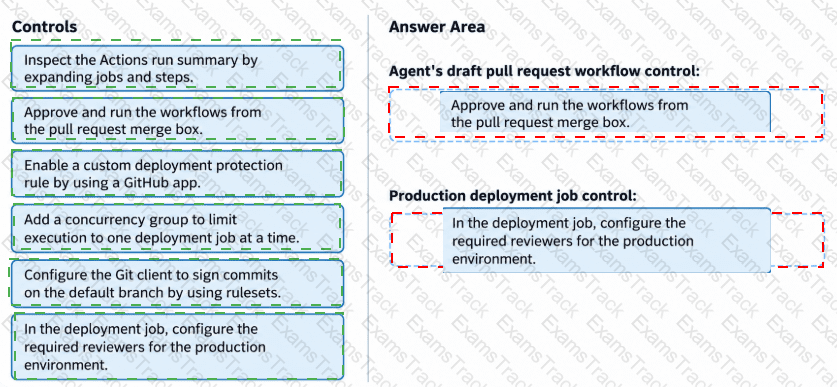
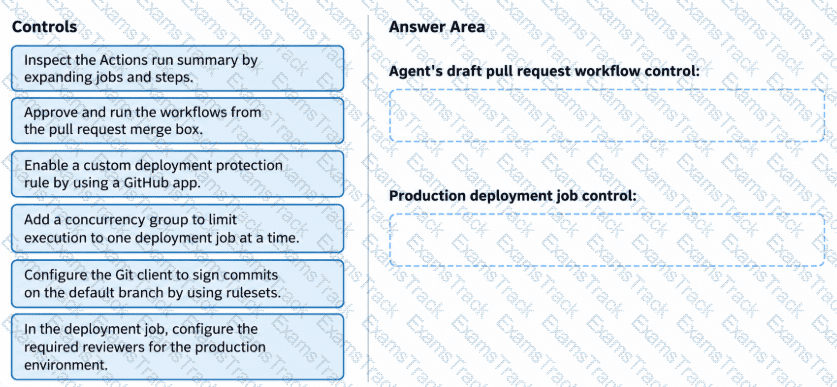
You have a GitHub Enterprise Cloud repository that uses the GitHub Copilot coding agent to resolve backlog issues by creating draft pull requests. The repository uses a GitHub Actions workflow for deployments to the production environment.
You discover that the workflow is being triggered before human review.
You need to configure GitHub controls to meet the following requirements:
The workflow for the agent’s draft pull requests must NOT run until a user that has write access approves the pull requests.
Production deployment jobs must start only after a user with write access explicitly approves the jobs.
Which controls should you configure? To answer, drag the appropriate controls to the correct requirements.
You need to resolve the issue of the agents generating conflicting output. The solution must meet the implementation guidelines.
What should you do?
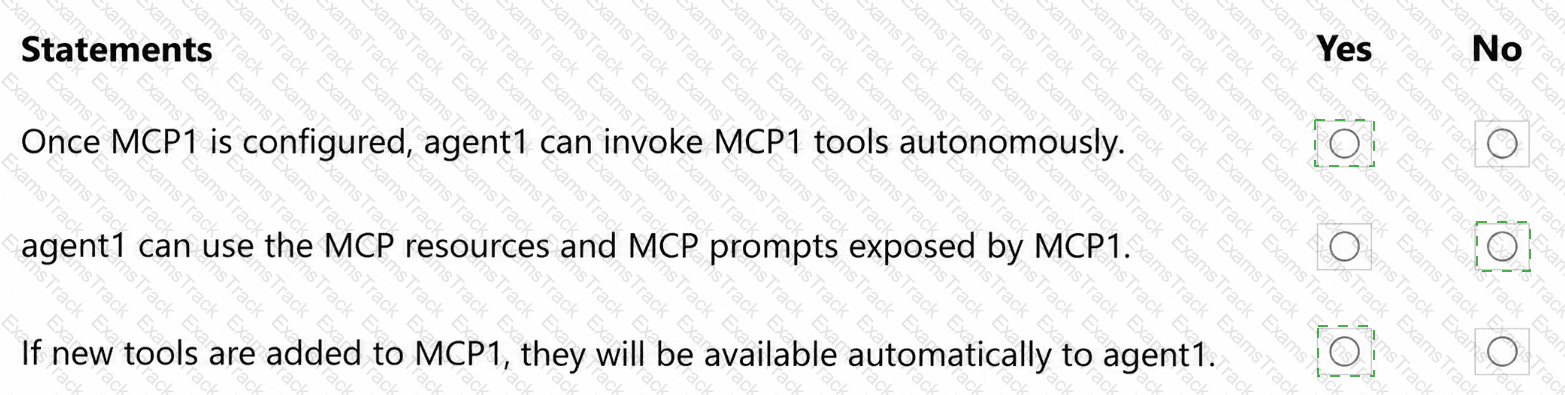
You are evaluating how agent1 will behave after you implement the planned changes.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
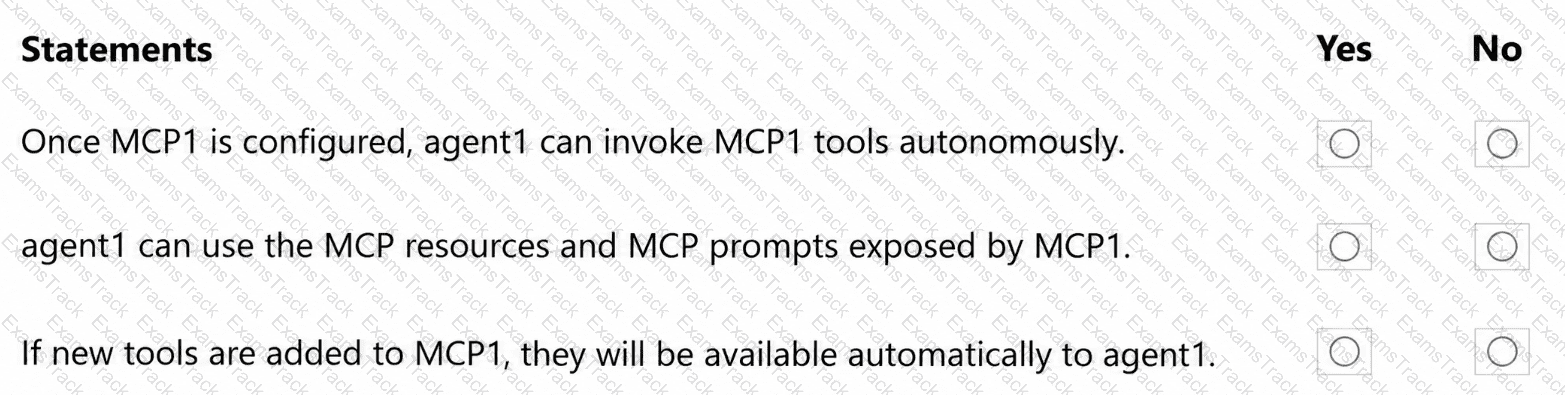
You need to configure agent1 to support the planned changes.
What should you do?
You need to provide access to the API key of MCP1. The solution must meet the security requirements.
What should you do?
You need to resolve the scoping issue associated to agent1.
What should you do?
|
PDF + Testing Engine
|
|---|
|
$43.75 |
|
Testing Engine
|
|---|
|
$33.75 |
|
PDF (Q&A)
|
|---|
|
$28.75 |
Microsoft Free Exams |
|---|
|
Copyright © 2026 Examstrack. All Rights Reserved
TESTED 20 Sep 2026