examstrack logo
You are reviewing a report from your FortiWeb logs and notice a JavaScript payload like < script > document.cookie < /script > is submitted through a product review form. The page doesn’t filter the script, and when users view the review, their session cookies are exposed.
Why is this attack dangerous?
Refer to the exhibit.
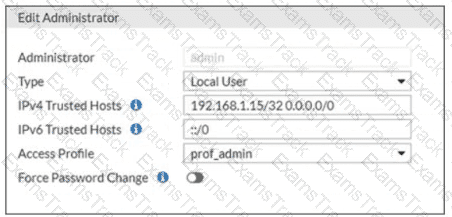
There is only one administrator account configured on FortiWeb and IPv6 is not configured on any interface.
Which action should an administrator take to restrict any brute force attacks that attempt to gain access to the FortiWeb management GUI?
While reviewing FortiWeb logs, you notice a suspicious login request that failed authentication. You suspect it may be part of an injection attack targeting the login form.
Which input pattern is an example of a typical SQL injection attempt that could bypass authentication checks?
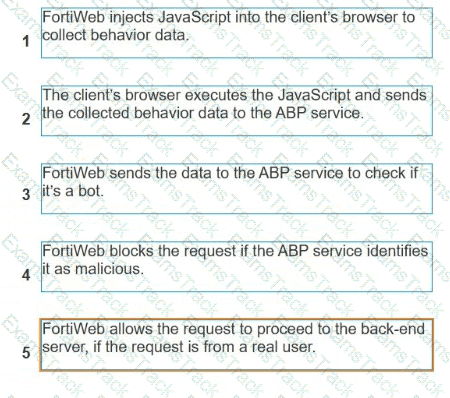
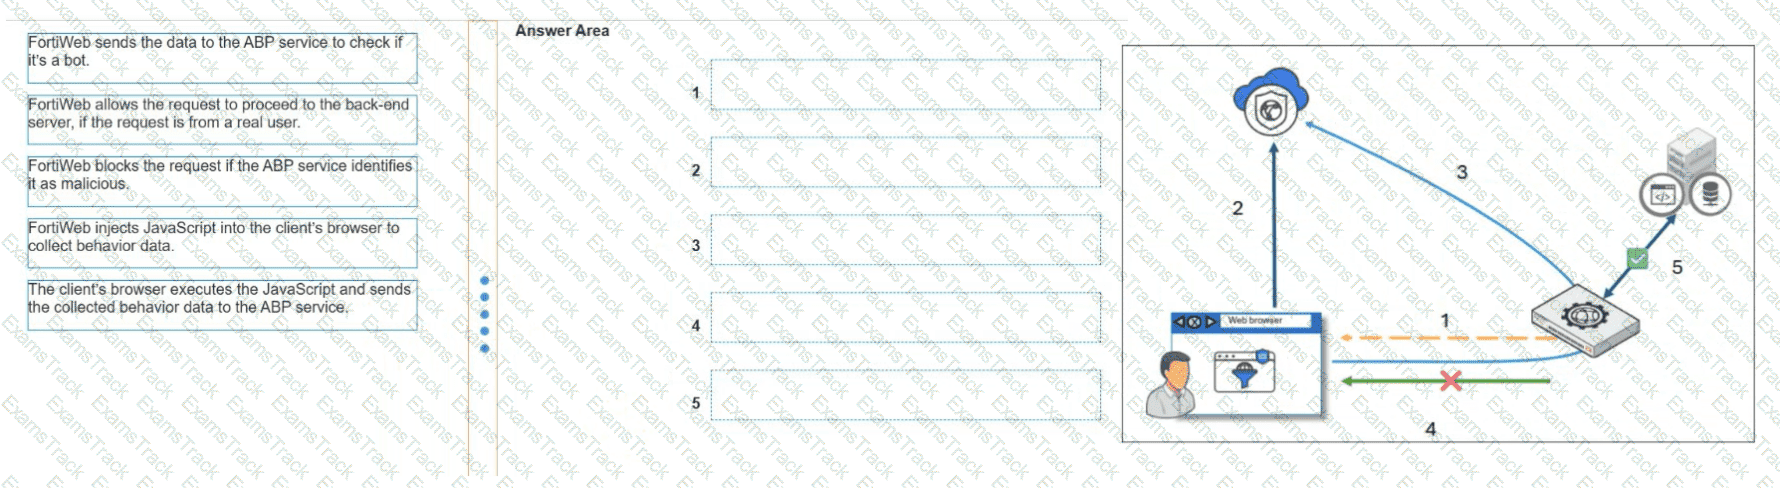
You are reviewing the FortiWeb integration with the Advanced Bot Protection (ABP) service.
Match each step in the ABP flow with its description.
A FortiWeb administrator wants to create a machine learning (ML)-based bot detection system.
Which three actions must the administrator take to build and activate this ML model? (Choose three.)
Your team is spending too much time digging through FortiWeb logs to investigate threats.
How can FortiAI improve this workflow?
Which situation best explains when a FortiWeb administrator should enable automatic HTTP-to-HTTPS redirection?
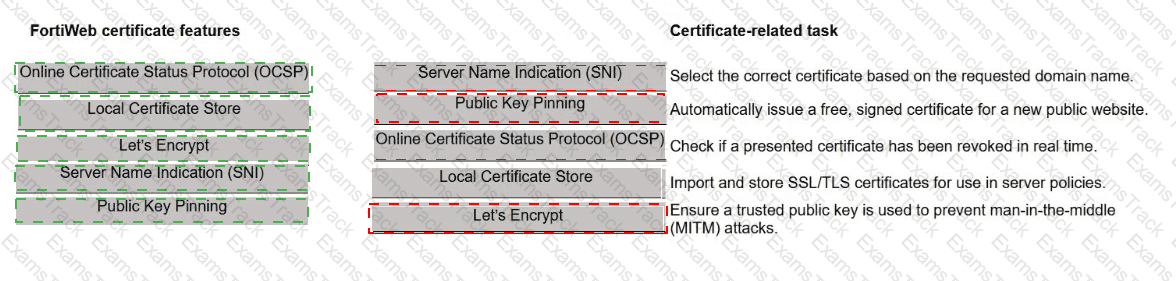
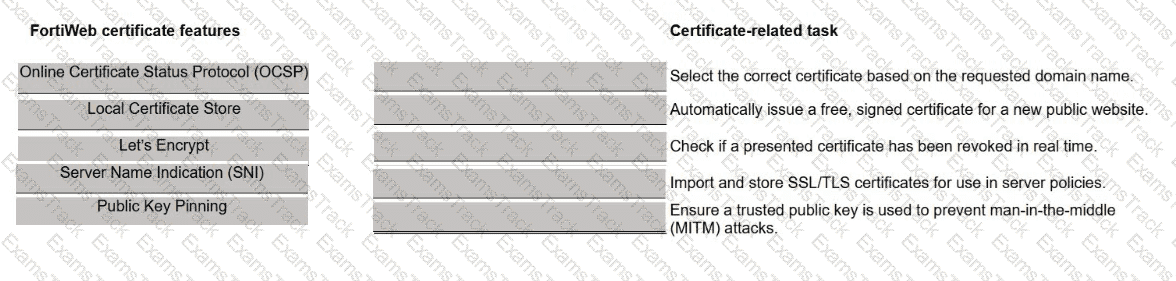
You are working on securing HTTPS communication across different services using FortiWeb. Your task is to configure and validate digital certificates for various traffic and communication needs.
Match each FortiWeb certificate feature to the certificate-related task that supports the feature.
Refer to the exhibits.
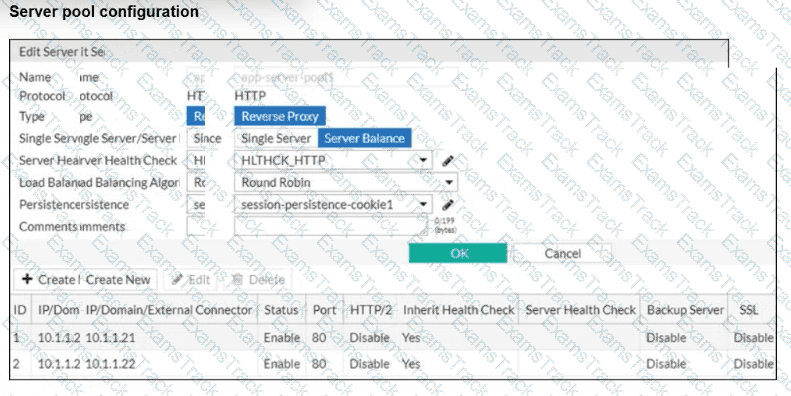
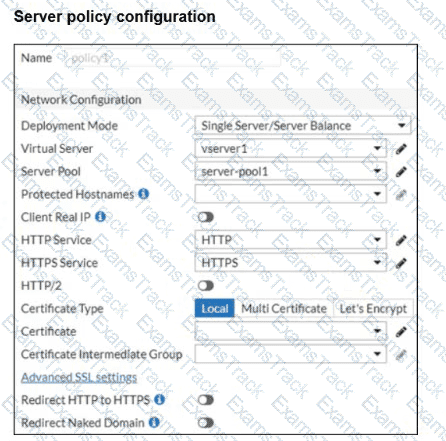
You are configuring a FortiWeb device in reverse proxy mode, placed downstream from a FortiGate. The server pool includes two back-end web servers: 10.1.1.21 and 10.1.1.22, and you’ve defined a health check policy.
After completing the server policy configuration and applying it to a virtual server, you notice that FortiWeb is not forwarding traffic to the back-end servers. No errors or health check failures appear in the logs.
Based on the configuration shown in the exhibit, which change should you make to restore back-end traffic flow?
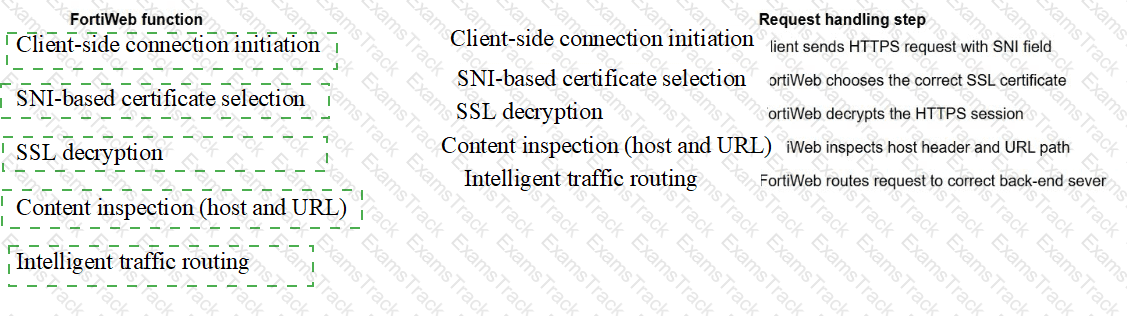
You are setting up a FortiWeb policy to protect a customer login portal. Users connect to https://login.training.lab, and you want FortiWeb to forward those requests to a load-balanced pool of back-end servers.
Which three components must you configure to complete the server policy?
|
PDF + Testing Engine
|
|---|
|
$41.25 |
|
Testing Engine
|
|---|
|
$31.25 |
|
PDF (Q&A)
|
|---|
|
$26.25 |
Fortinet Free Exams |
|---|
|
Copyright © 2026 Examstrack. All Rights Reserved
TESTED 03 Oct 2026